How WordPress User Roles Shape Security, Collaboration, and Control
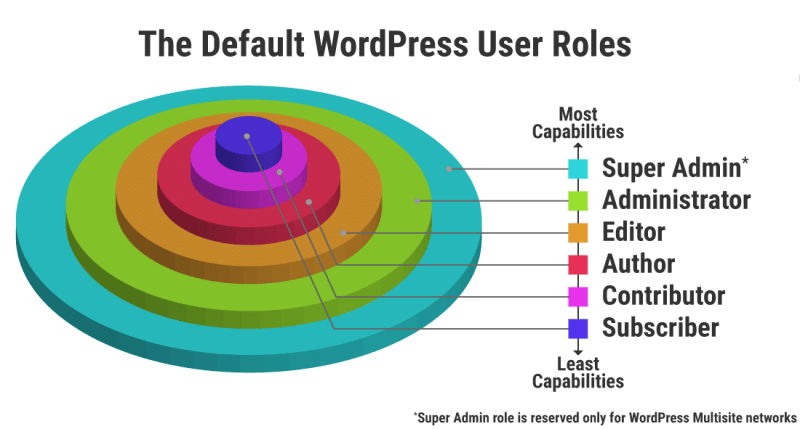
WordPress user roles are the invisible architecture of every multi-user site—determining who can publish content, approve plugins, or even delete themes. Yet despite their critical function, most administrators treat them as a checkbox rather than a strategic system. The default roles (Subscriber, Contributor, Author, Editor, Administrator) are just the starting point; custom capabilities and hierarchical structures can transform a chaotic team environment into a precision-controlled workflow. Whether managing a news outlet, an e-commerce platform, or a membership portal, the way you assign WordPress user roles directly impacts security, productivity, and scalability.
The problem isn’t a lack of documentation—it’s a lack of context. Many guides reduce WordPress user roles to a list of checkboxes, ignoring how roles interact with plugins, themes, and custom post types. For example, an Editor might have full control over standard posts but be locked out of WooCommerce product management unless explicitly granted capabilities. The same applies to multisite networks, where super admins wield authority over subsites while site admins remain constrained. These nuances explain why 68% of WordPress security breaches stem from misconfigured permissions, according to Wordfence’s 2023 report.
What follows is an analysis of how WordPress user roles function as both a technical framework and a collaborative tool—how they’ve evolved, how to leverage them effectively, and where the system may be heading. The goal isn’t to regurgitate the default roles but to expose the mechanics, real-world applications, and often-overlooked capabilities that turn a basic CMS into a fortress of controlled access.

The Complete Overview of WordPress User Roles
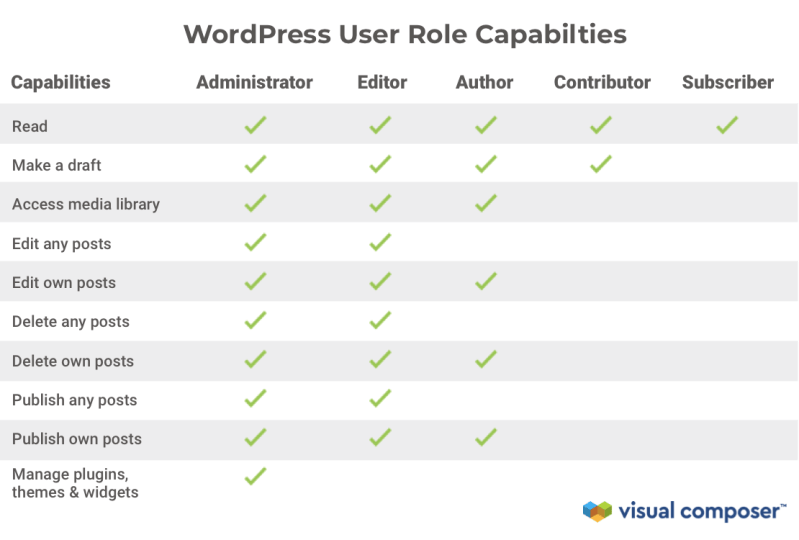
At its core, the WordPress user roles system is a role-based access control (RBAC) model designed to balance flexibility with granularity. Unlike rigid permission systems (e.g., Unix file permissions), WordPress roles are hierarchical yet extensible—allowing administrators to assign capabilities dynamically. Each role is a collection of predefined permissions (capabilities), which can be modified via plugins like User Role Editor or Members. For instance, while an Editor can publish and manage posts, they lack the `delete_users` capability unless explicitly granted, making them inherently safer than Administrators.The system’s strength lies in its modularity. Roles aren’t static; they can be combined, split, or overridden. A real estate agency might create a "Property Manager" role with access to custom post types (e.g., Listings) but restricted from modifying theme files. Similarly, a university website could grant "Course Instructors" the ability to edit course content while blocking them from user management. This adaptability is why WordPress user roles are the backbone of collaborative environments—from editorial teams to distributed development squads.
Historical Background and Evolution
The concept of WordPress user roles emerged in WordPress 2.0 (2005), when Matt Mullenweg and Mike Little introduced the first five roles to address the needs of bloggers and early multisite networks. The original roles—Subscriber, Contributor, Author, Editor, and Administrator—were designed for simplicity, with each level building on the previous one. Subscribers could only manage their profiles, while Administrators had unrestricted access. This tiered approach mirrored the hierarchical nature of traditional publishing, where editors reviewed content before it reached authors.The real turning point came with WordPress 3.0 (2010) and the introduction of multisite support. Suddenly, WordPress user roles had to account for network-wide administration, leading to the addition of the "Super Admin" role. This role could manage plugins and themes across all subsites, while individual site admins remained confined to their domains. The evolution didn’t stop there: plugins like Advanced Access Manager (AAM) and Members expanded capabilities, allowing administrators to create roles like "Affiliate" or "Moderator" with bespoke permissions. Today, the system supports over 300 default capabilities, though most sites use fewer than 20.
Core Mechanisms: How It Works
Under the hood, WordPress user roles rely on two interconnected systems: roles and capabilities. A role is a predefined bundle of capabilities (e.g., `edit_posts`, `manage_options`), while capabilities are the atomic permissions that determine what a user can do. When a user logs in, WordPress checks their role against the capabilities required for an action—such as editing a post or installing a plugin. If the capability exists in their role’s bundle, the action is permitted; otherwise, it’s denied.Table of Contents
- The Complete Overview of WordPress User Roles
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I create a custom role without plugins?
- Q: How do I restrict a role to specific post types?
- Q: What’s the difference between a role and a capability?
- Q: Can I import/export role settings across sites?
- Q: How do multisite roles differ from single-site roles?
- Q: Are there security risks with custom roles?
The system also employs hierarchy to simplify management. For example, an Editor inherits all capabilities of a Contributor but gains additional ones (e.g., `edit_others_posts`). This hierarchy reduces redundancy when assigning permissions. However, the real power comes from capability overrides. Plugins like User Role Editor allow administrators to add or remove capabilities from roles dynamically. For instance, you could strip the `publish_posts` capability from an Author, forcing them to submit drafts for Editor approval—a common workflow in legal or medical publishing.
Key Benefits and Crucial Impact
The strategic use of WordPress user roles isn’t just about security—it’s about aligning technical control with business processes. A poorly configured role system can lead to bottlenecks (e.g., an Editor waiting for an Administrator to approve a plugin) or vulnerabilities (e.g., a Contributor accidentally exposing sensitive data). Conversely, a well-structured role setup enhances collaboration, reduces friction, and minimizes risks. For example, a news site using custom roles for "Reporters," "Editors," and "Fact-Checkers" can ensure articles are reviewed without granting unnecessary access to the CMS backend.The impact extends beyond internal teams. E-commerce stores, for instance, often create roles like "Vendor" or "Warehouse Manager" to delegate order processing without exposing financial data. Similarly, membership sites use roles to gate content based on subscription tiers. The result? A scalable, audit-friendly system that grows with the site’s needs. As one WordPress security expert noted:
"Permissions aren’t just technical—they’re the first line of defense against both human error and malicious intent. A site with 100 users but only three roles is like a bank with one vault key: it’s only a matter of time before something goes wrong." — Sarah Gooding, WP Tavern
Major Advantages
- Granular Security: Limits exposure by restricting capabilities to only what’s necessary. For example, a role with `edit_theme_options` but no `delete_plugins` cannot compromise the site’s integrity.
- Workflow Optimization: Roles like "Editor" or "Contributor" enforce editorial processes (e.g., draft approvals) without manual oversight.
- Scalability: Custom roles adapt to new features (e.g., WooCommerce, LearnDash) without requiring role overhauls.
- Audit Trails: Role-based actions are logged in WordPress’s user activity system, making it easier to track changes.
- Plugin/Theme Compatibility: Many premium plugins (e.g., BuddyPress, Gravity Forms) integrate with WordPress user roles, allowing role-specific functionality.
Comparative Analysis
While WordPress’s default roles cover most use cases, third-party solutions offer deeper customization. Below is a comparison of native roles versus plugin-enhanced approaches:| Native WordPress Roles | Plugin-Enhanced Roles (e.g., AAM, Members) |
|---|---|
|
|
Future Trends and Innovations
The WordPress user roles system is poised for evolution, driven by two key trends: AI-driven automation and decentralized access control. AI could soon analyze user behavior to suggest role adjustments—e.g., flagging an Editor who frequently requests plugin access as a candidate for promotion. Meanwhile, blockchain-based identity verification (via plugins like Blockchain Identity) may introduce roles tied to verified credentials, replacing password-based authentication with cryptographic proofs.Another frontier is role-based APIs. As WordPress embraces headless architectures, roles could determine API access levels (e.g., a "Content Consumer" role with read-only endpoints). This would align with the rise of JAMstack setups, where backend permissions dictate frontend data exposure. The challenge? Balancing innovation with backward compatibility—ensuring new features don’t break legacy sites.
Conclusion
WordPress user roles are more than a permission checklist; they’re the foundation of a site’s governance. Whether you’re securing a client portal, streamlining a newsroom, or scaling an e-commerce store, the way you configure roles determines who can do what—and who can’t. The default roles are a starting point, but the real power lies in understanding capabilities, leveraging plugins, and adapting to your workflow’s unique needs.The future of WordPress user roles will likely blend automation with granularity, reducing manual overhead while increasing precision. For now, the key takeaway is simple: treat roles as a strategic tool, not a technical afterthought. A well-structured role system isn’t just secure—it’s a force multiplier for productivity.
Comprehensive FAQs
Q: Can I create a custom role without plugins?
A: Yes, but it requires PHP. Use the `add_role()` function in your theme’s `functions.php` or a custom plugin. Example:
```php
add_role('property_manager', 'Property Manager', array(
'edit_posts' => true,
'delete_published_posts' => false,
'manage_options' => false
));
```
For most users, plugins like User Role Editor are simpler.
Q: How do I restrict a role to specific post types?
A: Plugins like Advanced Access Manager allow role-based post type restrictions. Alternatively, use the `map_meta_cap` filter to override capabilities dynamically. Example:
```php
function restrict_custom_post_type($caps, $cap, $user_id, $args) {
if ($cap === 'edit_post' && $args[0] === 'listing') {
$user = new WP_User($user_id);
if (!$user->has_cap('edit_listings')) $caps = array();
}
return $caps;
}
add_filter('map_meta_cap', 'restrict_custom_post_type', 10, 4);
Q: What’s the difference between a role and a capability?
A: A role is a bundle of capabilities (e.g., "Editor" includes `publish_posts`). A capability is a single permission (e.g., `edit_users`). Roles simplify management, while capabilities enable granular control. Think of roles as job titles and capabilities as specific tasks within that job.
Q: Can I import/export role settings across sites?
A: Yes, use plugins like WP All Import/Export or WP Migrate DB to transfer role data. For custom roles, export the `wp_usermeta` table (where roles are stored) via phpMyAdmin or a database backup tool.
Q: How do multisite roles differ from single-site roles?
A: Multisite introduces the Super Admin role, which manages network-wide settings (plugins, themes, users). Site Admins (equivalent to single-site Admins) are confined to their subsite. Subscribers in multisite can only access their profile unless granted broader permissions via plugins like Multisite Role Manager.
Q: Are there security risks with custom roles?
A: Yes. Overly permissive custom roles (e.g., granting `manage_options` to a non-Admin) can create vulnerabilities. Always audit capabilities with tools like WP Security Audit Log and follow the principle of least privilege—grant only what’s necessary.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.