Unseen Risks: How to Outmaneuver Threats With Comprehensive Strategies to Mitigate Invisible Dangers
The most dangerous threats are the ones you never see coming. Not the headline-grabbing cyberattacks or the predictable supply chain disruptions, but the silent, systemic risks that erode stability from within—until it’s too late. These are the invisible threats: the unmonitored data leaks in legacy systems, the unchecked third-party dependencies that become backdoors, the cultural blind spots that render even the most robust protocols ineffective. Mitigating them requires more than reactive firewalls or compliance checklists; it demands a comprehensive strategy that anticipates the unseen, dismantles assumptions, and hardens systems against what hasn’t happened yet.
Organizations spend billions on visible defenses—encryption, intrusion detection, physical security—but the real vulnerabilities lie in the gaps between what’s measured and what’s ignored. A 2023 study by the Ponemon Institute revealed that 68% of breaches originate from unidentified or misclassified risks, yet only 12% of security budgets allocate resources to proactive threat hunting. The discrepancy isn’t just financial; it’s existential. Invisible threats don’t announce themselves. They exploit the absence of attention.
Consider the case of a global retailer that lost $47 million in a single incident—not to hackers, but to a supply chain misconfiguration. A single vendor’s unpatched IoT device became a pivot point for a ransomware strain that propagated through the retailer’s entire logistics network. The attack wasn’t sophisticated; it was invisible. No alerts, no anomalies, just a cascade of failures rooted in overlooked dependencies. The lesson? The most effective threats comprehensive strategies mitigate invisible threats are those that treat risk as a dynamic ecosystem, not a static checklist.
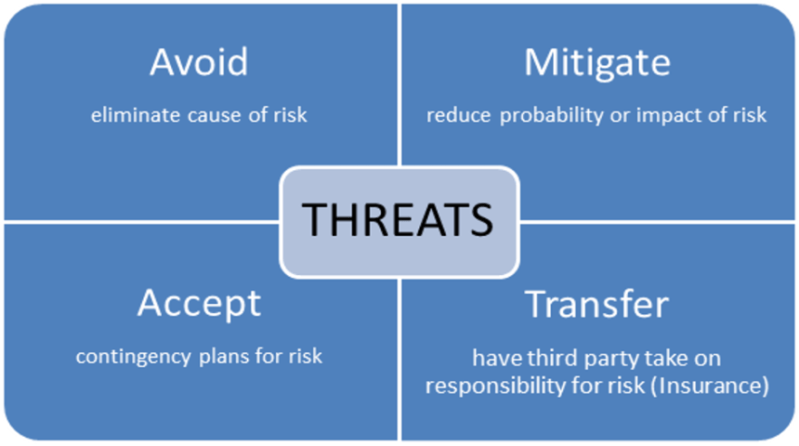
The Complete Overview of Threats Comprehensive Strategies Mitigate Invisible
The problem with invisible threats is that they defy traditional risk models. Firewalls can’t stop what’s never logged; audits can’t uncover what’s never audited. These risks thrive in the negative space—the unstructured data, the unmonitored interactions, the human behaviors that bypass protocols. A comprehensive strategy to mitigate invisible threats must operate on three fronts: detection (finding what’s hidden), prevention (closing the gaps before exploitation), and resilience (limiting damage when detection fails). The goal isn’t perfection—it’s reducing the attack surface of the unseen.
Historically, risk mitigation focused on known threats. Firewalls blocked IP ranges, antivirus scanned for signatures, and compliance frameworks enforced static rules. But invisible threats—whether zero-day exploits, insider negligence, or third-party vulnerabilities—operate outside these parameters. The shift toward proactive threat intelligence and behavioral analytics marks the evolution from reactive defense to predictive resilience. Today’s strategies must account for the invisible vectors that traditional tools miss: the unencrypted email threads, the shadow IT deployments, the cultural norms that treat security as an afterthought.
Historical Background and Evolution
The concept of mitigating invisible threats emerged from the ashes of high-profile failures where visibility was the critical missing link. The 2013 Target breach, for instance, wasn’t stopped by a breach in the retailer’s systems but by a vendor’s unsecured HVAC system. The attack vector was invisible to Target’s security team because it wasn’t part of their monitored infrastructure. This incident forced a reckoning: comprehensive strategies must extend beyond the organization’s perimeter to include the entire ecosystem of dependencies. The rise of threat hunting—actively searching for unknown risks—became a necessity, not a luxury.
Table of Contents
- The Complete Overview of Threats Comprehensive Strategies Mitigate Invisible
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do I identify invisible threats in my organization?
- Q: What’s the biggest misconception about mitigating invisible threats?
- Q: Can small businesses afford to implement these strategies?
- Q: How often should I update my invisible threat mitigation strategy?
- Q: What’s the first step if I suspect an invisible threat has already compromised my systems?
Fast-forward to 2020, and the COVID-19 pandemic exposed another layer of invisible risk: operational fragility. Companies that assumed their remote-work policies were secure found themselves vulnerable to phishing-as-a-service and unpatched VPNs. The shift to hybrid work didn’t just change where employees sat; it redefined the attack surface. Invisible threats like deepfake voice scams or AI-driven social engineering now exploit the gaps between human behavior and technological controls. The lesson? Mitigation strategies must evolve alongside the threats—from static rules to adaptive, context-aware systems.
Core Mechanisms: How It Works
A comprehensive strategy to mitigate invisible threats relies on three interconnected mechanisms: contextual awareness, automated anomaly detection, and human-in-the-loop validation. Contextual awareness means understanding not just what’s happening, but why—whether a login attempt is anomalous because it’s from a new device, a new location, or a new behavior pattern. Automated anomaly detection uses machine learning to flag deviations from baseline activity, while human validation ensures false positives don’t drown out real risks. The most effective systems don’t just alert—they explain the risk and suggest remediation.
The second mechanism is dependency mapping—a systematic approach to identifying and assessing the risks posed by third parties, vendors, and even internal teams. Traditional risk assessments treat dependencies as binary (secure/not secure), but invisible threats exploit the gradations of risk. A vendor with a single unpatched system can become a pivot point for an entire network. By mapping these dependencies in real-time and applying dynamic risk scoring, organizations can prioritize mitigation efforts where they matter most. The key is treating dependencies as part of the threat landscape, not an afterthought.
Key Benefits and Crucial Impact
The stakes of ignoring invisible threats are clear: financial loss, reputational damage, and operational paralysis. But the benefits of a comprehensive strategy to mitigate invisible threats extend beyond avoidance. They include proactive resilience, where organizations don’t just react to incidents but prevent them before they escalate. They also enable strategic agility—the ability to pivot quickly when new threats emerge without being bogged down by legacy vulnerabilities. The most forward-thinking companies aren’t just protecting data; they’re safeguarding their ability to innovate.
Consider the case of a financial institution that implemented a real-time dependency monitoring system. Within six months, they identified and patched a critical vulnerability in a third-party payment processor—before it was exploited. The cost? A fraction of what a breach would have incurred. The return? Not just financial, but competitive—a reputation for security that attracts clients and talent. Invisible threats don’t just disappear when mitigated; they become competitive differentiators.
"The greatest threat to an organization isn’t the attack itself—it’s the assumption that it won’t happen."
— Gartner, 2023 Threat Intelligence Report
Major Advantages
- Reduced Blind Spots: Proactive threat hunting and dependency mapping eliminate the "unknown unknowns" that traditional security misses.
- Faster Incident Response: Automated detection and contextual alerts allow teams to act before damage spreads.
- Cost Efficiency: Preventing a single breach can save millions—far outweighing the investment in mitigation tools.
- Regulatory Compliance: Many frameworks (e.g., NIST, ISO 27001) now require invisible threat mitigation as a core component.
- Competitive Edge: Organizations that master comprehensive strategies gain trust with clients, partners, and investors.

Comparative Analysis
| Traditional Security | Invisible Threat Mitigation |
|---|---|
| Focuses on known threats (e.g., malware, SQL injection). | Targets unknown vectors (e.g., shadow IT, insider negligence, third-party risks). |
| Relies on static rules (firewalls, AV signatures). | Uses adaptive analytics (AI, behavioral modeling, real-time dependency mapping). |
| Measures success by breach prevention. | Measures success by resilience—limiting impact even if a breach occurs. |
| Budget allocated to reactive tools (e.g., IDS, SIEM). | Budget allocated to proactive threat intelligence and continuous monitoring. |
Future Trends and Innovations
The next frontier in threats comprehensive strategies mitigate invisible threats lies in predictive resilience—using AI to not just detect risks but forecast them. Machine learning models trained on historical attack patterns can now simulate potential breaches and recommend preemptive actions. Meanwhile, quantum-resistant encryption is becoming a necessity as quantum computing threatens to obsolete current cryptographic standards. The shift toward zero-trust architectures—where every access request is treated as a potential threat—will further reduce reliance on perimeter-based defenses.
Another emerging trend is human-centric security—recognizing that the biggest invisible threat is often people. Phishing, social engineering, and insider threats account for over 90% of breaches. Future strategies will integrate behavioral psychology into risk mitigation, using nudges and training to reinforce secure habits. The goal isn’t just to secure systems but to change the culture around risk. As threats become more invisible, the most resilient organizations will be those that treat security as a dynamic discipline, not a static process.

Conclusion
The invisible threats of today are the comprehensive strategies of tomorrow. The organizations that thrive won’t be those with the most firewalls, but those with the deepest understanding of what they can’t see. Mitigation isn’t about building higher walls; it’s about illuminating the dark corners where risks hide. The tools exist—threat intelligence platforms, dependency analyzers, AI-driven anomaly detection—but success depends on cultural adoption. Security teams must shift from defenders to hunters, from reactive responders to proactive strategists.
The choice is clear: ignore invisible threats and risk catastrophic failure, or embrace comprehensive strategies to mitigate invisible dangers before they materialize. The difference between the two isn’t technology—it’s mindset. And in the world of unseen risks, mindset is the most powerful defense of all.
Comprehensive FAQs
Q: How do I identify invisible threats in my organization?
A: Start with a dependency audit—map all third-party vendors, internal teams, and shadow IT systems. Use threat intelligence feeds to cross-reference known vulnerabilities, then deploy behavioral analytics to detect anomalies in user activity. Tools like MITRE ATT&CK and NIST’s Cybersecurity Framework provide structured methodologies for hunting unknown risks.
Q: What’s the biggest misconception about mitigating invisible threats?
A: Many assume that comprehensive strategies require massive budgets or overhauling existing systems. In reality, the most effective mitigation starts with visibility—simple steps like logging all access attempts, monitoring vendor changes, and training teams to recognize unusual patterns can drastically reduce exposure.
Q: Can small businesses afford to implement these strategies?
A: Absolutely. While enterprise-grade tools exist, smaller organizations can leverage open-source threat intelligence (e.g., AlienVault OTX, MISP) and cloud-based dependency scanners (e.g., SecurityScorecard). The key is prioritizing high-impact, low-cost measures like multi-factor authentication, vendor risk assessments, and employee training.
Q: How often should I update my invisible threat mitigation strategy?
A: At least quarterly, but ideally in real-time. Threat landscapes evolve daily—new exploit techniques, vendor breaches, and regulatory changes all demand continuous adaptation. Automated threat feeds and red team exercises can help keep strategies dynamic.
Q: What’s the first step if I suspect an invisible threat has already compromised my systems?
A: Isolate affected systems immediately, then conduct a forensic analysis to determine the scope. Engage a third-party incident responder to avoid bias, and use the findings to harden your comprehensive strategy. The goal isn’t just containment—it’s preventing recurrence by addressing the root cause (e.g., unpatched software, misconfigured dependencies).
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.