Navigating Digital Privacy Content Landscapes Regional: A Global Breakdown
The European Union’s GDPR doesn’t just protect data—it redefines how content is created, distributed, and monetized across borders. While Western platforms default to opt-in consent models, Chinese social media giants like WeChat embed user tracking into their core infrastructure, creating a digital privacy content landscapes regional where personalization and surveillance coexist. Meanwhile, in the Middle East, platforms like Mubasher adapt to Islamic finance regulations, blending financial privacy with cultural norms. These aren’t isolated cases; they’re symptoms of a fragmented global system where privacy standards are as diverse as the jurisdictions enforcing them.
Regional digital privacy frameworks don’t operate in a vacuum. They’re shaped by geopolitical tensions—take the U.S.-China tech war, where Huawei’s global bans forced regional adaptations in data localization laws—or by economic pressures, like India’s 2023 Digital Personal Data Protection Act, which balances Silicon Valley’s lobbying with domestic sovereignty demands. Even within the EU, member states interpret GDPR differently: Germany’s strict stance on biometric data clashes with Hungary’s relaxed enforcement, creating digital privacy content landscapes regional that confuse businesses and users alike.
Content creators, marketers, and tech firms now face a paradox: globalize reach while complying with 195+ distinct legal regimes. A single ad campaign might need GDPR-compliant cookie banners in Brussels, age-gate verifications in Singapore, and censored keywords in Russia. The result? A patchwork of regional digital privacy content ecosystems where innovation thrives in some markets and stifles in others. Understanding these dynamics isn’t optional—it’s the difference between a seamless user experience and a legal nightmare.
The Complete Overview of Digital Privacy Content Landscapes Regional
The term digital privacy content landscapes regional refers to the intersection of jurisdictional privacy laws, platform policies, and cultural expectations that dictate how digital content is produced, shared, and governed. Unlike the monolithic "internet" of the 2000s, today’s digital sphere is a mosaic of regulated zones where data flows are gated by everything from free speech laws to state-backed censorship. For example, a TikTok video in Dubai might auto-blur faces to comply with UAE’s strict privacy rules, while the same content in Berlin would trigger GDPR’s "right to be forgotten" requests if requested.
This fragmentation isn’t accidental. It’s the result of three decades of policy experimentation: from the EU’s 1995 Data Protection Directive to China’s 2021 Personal Information Protection Law (PIPL), each region has crafted its own balance between innovation and control. The consequences ripple through every layer of the digital stack—from cloud providers like AWS choosing data centers based on sovereignty laws to journalists using encrypted tools like Signal to bypass regional surveillance. Even algo-driven content recommendation systems (e.g., YouTube’s feed) are now regionally calibrated, adjusting for local privacy sensitivities around topics like health data or political dissent.
Historical Background and Evolution
The modern era of digital privacy content landscapes regional began in the 1990s, when the U.S. and EU clashed over data transfers under the Safe Harbor framework. The 2000 collapse of Safe Harbor forced the EU to develop GDPR’s predecessor, leading to a wave of regional laws that treated data as a territorial resource. By 2010, Brazil’s Marco Civil da Internet and Canada’s PIPEDA emerged, followed by China’s 2017 Cybersecurity Law—a watershed moment where privacy became a tool of state control rather than individual rights.
Table of Contents
- The Complete Overview of Digital Privacy Content Landscapes Regional
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do regional privacy laws affect cross-border content distribution?
- Q: Can businesses ignore regional digital privacy content landscapes?
- Q: How do authoritarian regimes use digital privacy laws for control?
- Q: What’s the biggest misconception about regional digital privacy?
- Q: How are emerging markets shaping digital privacy content landscapes?
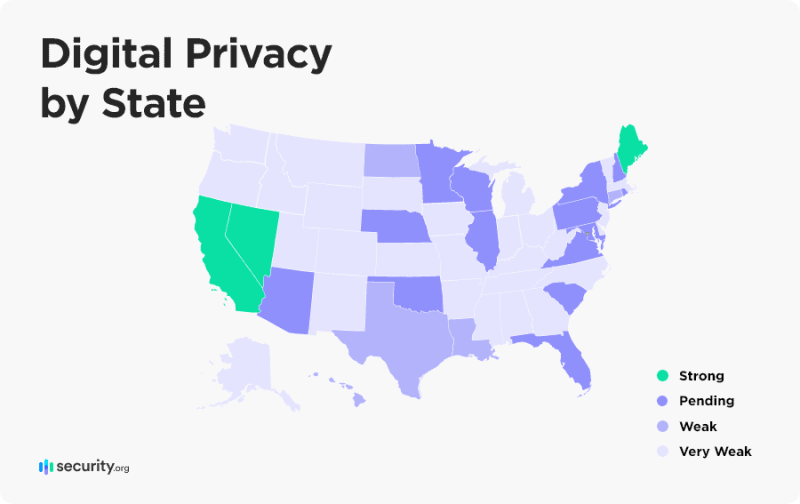
Fast-forward to 2023, and the landscape has atomized further. The U.S. lacks federal privacy legislation, leaving states like California (CCPA) and Virginia (CDPA) to set their own rules, while the UK’s post-Brexit Data Protection Act diverged from GDPR. Meanwhile, Africa’s digital privacy content ecosystems are evolving rapidly: Nigeria’s 2023 Data Protection Act mirrors GDPR in structure but faces enforcement challenges, while Kenya’s 2019 law prioritizes local data storage. These shifts reflect deeper trends—rising nationalism, tech sovereignty movements, and the weaponization of data in conflicts (e.g., Russia’s use of Telegram bans during the Ukraine war).
Core Mechanisms: How It Works
At the technical level, digital privacy content landscapes regional are enforced through a combination of jurisdictional triggers, platform compliance modules, and user-level adaptations. Jurisdictional triggers include IP-based geofencing (e.g., blocking VPNs in China), domain restrictions (e.g., .eu sites requiring GDPR compliance), or metadata flags (e.g., Arabic-language content scanned for offensive terms in Gulf states). Platforms like Google and Meta deploy compliance modules—automated systems that adjust content delivery based on regional laws, such as hiding ads for gambling in Singapore or age-verifying users in Germany.
User-level adaptations are often invisible but critical. For instance, a WhatsApp user in India might see end-to-end encryption by default, while a user in the UAE could face mandatory data localization prompts. Even seemingly neutral tools like Google Analytics are configured differently across regions: in the EU, it’s pre-configured for GDPR’s "Do Not Sell My Data" links, while in the U.S., it defaults to opt-out models. The result is a dynamic privacy infrastructure where content isn’t just filtered—it’s reconstructed to fit local legal and cultural contexts.
Key Benefits and Crucial Impact
The regionalization of digital privacy has reshaped power dynamics in the tech industry. For users, it offers tangible protections: GDPR’s right to access personal data has led to a 40% reduction in unsolicited marketing in the EU, while India’s 2023 law gives citizens the right to demand deletion of biometric data. For businesses, compliance with digital privacy content landscapes regional has become a competitive advantage—companies like Apple and Microsoft leverage their privacy-first branding to attract EU and APAC customers wary of Chinese surveillance capitalism.
Yet the impact isn’t uniformly positive. In authoritarian regimes, regional privacy laws become tools of control. Russia’s 2022 "foreign agent" law for digital platforms forces transparency that enables censorship, while China’s PIPL requires foreign firms to hand over user data to local authorities—a practice that has led to mass surveillance in Xinjiang. Even in democratic regions, the fragmentation creates compliance costs: a 2023 study by the IAPP found that multinational firms spend an average of $12 million annually navigating regional digital privacy content ecosystems.
— Tim Wu, Columbia Law School
"Privacy laws are no longer about protecting individuals. They’re about geopolitical positioning. The EU uses GDPR to push back against U.S. tech dominance, while China uses its laws to export its surveillance model. The result? A digital Cold War where privacy is the battleground."
Major Advantages
- User Empowerment: Regional laws like GDPR and India’s DPDP give citizens explicit rights over their data, reducing exploitation by corporations and governments. For example, GDPR’s "right to erasure" has led to a 60% increase in data deletion requests in the EU.
- Market Differentiation: Companies like Signal and ProtonMail thrive by marketing their compliance with strict digital privacy content landscapes regional (e.g., Switzerland’s FADP law), attracting users from high-privacy regions.
- Innovation Safeguards: Laws like Brazil’s Marco Civil protect net neutrality, allowing local startups to compete with global giants without fear of algorithmic discrimination.
- Cultural Respect: Regional adaptations—such as Muslim-majority countries’ restrictions on biometric data—align tech products with local values, reducing backlash and improving adoption.
- Geopolitical Leverage: Privacy laws have become diplomatic tools. The EU’s GDPR influenced South Korea’s 2020 Personal Information Protection Act, while China’s PIPL pressures Southeast Asian nations to adopt similar frameworks.

Comparative Analysis
| Region | Key Features of Digital Privacy Content Landscapes Regional |
|---|---|
| European Union (GDPR) |
|
| China (PIPL) |
|
| United States (State-Level) |
|
| Middle East (Gulf States) |
|
Future Trends and Innovations
The next decade of digital privacy content landscapes regional will be defined by three forces: technological convergence, legal arbitrage, and cultural resistance. On the tech front, AI-driven compliance tools (e.g., automated GDPR audits) will reduce costs, but they’ll also enable more granular regional targeting—imagine a single website dynamically adjusting its cookie banners, age gates, and content filters based on a user’s geolocation and device fingerprint. Legal arbitrage will intensify as firms exploit loopholes in regional digital privacy ecosystems, such as routing data through jurisdictions with lax laws (e.g., Luxembourg’s "privacy haven" status) or using offshore entities to bypass localization rules.
Cultural resistance will manifest in unexpected ways. For instance, Gen Z in Latin America is pushing for "digital sovereignty" laws that reject U.S. and Chinese tech dominance, while African nations are developing pan-regional privacy frameworks to avoid over-reliance on Western models. Meanwhile, the rise of "privacy-enhancing computation" (e.g., federated learning, homomorphic encryption) could reduce the need for regional data transfers, but it may also create new compliance gray areas. One thing is certain: the era of a "one-size-fits-all" internet is over. The future belongs to context-aware digital privacy, where content, platforms, and laws adapt in real time to regional nuances.

Conclusion
The fragmentation of digital privacy content landscapes regional reflects a fundamental shift: privacy is no longer a universal right but a negotiated one, shaped by local laws, geopolitics, and cultural values. For businesses, this means embracing agility—whether through modular compliance systems or regional product variants. For users, it demands vigilance: what’s private in Berlin may be public in Beijing, and what’s encrypted in Switzerland could be surveilled in Singapore. The challenge ahead isn’t just navigating these landscapes but redefining what privacy means in a world where borders are as fluid as data flows.
Yet within this complexity lies opportunity. Regional privacy laws have forced innovation—from decentralized identity systems (e.g., Sovrin) to privacy-preserving advertising (e.g., Google’s Privacy Sandbox). The key will be balancing standardization (to reduce costs) with localization (to respect diversity). As Tim Wu noted, the digital privacy battleground is now a global chessboard. The players who adapt fastest to regional digital privacy content ecosystems will shape the rules of the next era.
Comprehensive FAQs
Q: How do regional privacy laws affect cross-border content distribution?
A: Regional laws create jurisdictional friction for cross-border content. For example, a video platform like YouTube must:
- Geoblock content in China due to censorship laws.
- Add GDPR-compliant cookie banners for EU users.
- Disable certain ad targeting in California under CCPA.
Q: Can businesses ignore regional digital privacy content landscapes?
A: No. Ignoring regional laws leads to:
- Legal penalties: GDPR fines up to 4% of global revenue.
- Operational bans: Google Maps was blocked in India for 2018 data localization violations.
- Reputational damage: Users in privacy-conscious regions (e.g., EU, Japan) avoid non-compliant brands.
Q: How do authoritarian regimes use digital privacy laws for control?
A: Authoritarian regimes exploit digital privacy content landscapes regional to:
- Enforce censorship: China’s PIPL requires platforms to remove "illegal" content, enabling state surveillance.
- Demand data access: Russia’s 2022 "foreign agent" law forces transparency, aiding intelligence operations.
- Restrict encryption: India’s 2023 DPDP allows government backdoors for "national security."
- Track dissent: UAE’s 2022 cybercrime law mandates real-name accounts, suppressing anonymous activism.
Q: What’s the biggest misconception about regional digital privacy?
A: The myth that stronger privacy laws equal better protection. For example:
- China’s PIPL is technically robust but prioritizes state access over individual rights.
- Russia’s 2016 "Yarovaya Law" bans VPNs, claiming privacy protections while enabling mass surveillance.
- Some African nations adopt GDPR-like laws but lack enforcement infrastructure.
Q: How are emerging markets shaping digital privacy content landscapes?
A: Emerging markets are redefining regional digital privacy ecosystems through:
- Localization demands: India’s DPDP requires data storage within the country, pushing firms to build regional servers.
- Cultural adaptations: Nigeria’s 2023 law exempts traditional medicine data from strict rules, reflecting local practices.
- Anti-colonial tech: Brazil’s Marco Civil prioritizes net neutrality to counter U.S. platform dominance.
- Regional alliances: African nations are developing the African Data Policy to avoid over-reliance on Western models.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.