How Data Lifecycle Management (DLM) Transforms Business: What Are the Three Main Goals?
Data isn’t just a corporate asset—it’s the lifeblood of decision-making, compliance, and competitive advantage. Yet, without structured oversight, raw data degrades into chaos: siloed repositories, redundant duplicates, and unchecked vulnerabilities. The question isn’t whether organizations need a disciplined approach to managing data’s journey from creation to disposal, but how they can align their strategies with the core objectives that define what are the three main goals of data lifecycle management (DLM)? These goals aren’t abstract concepts; they’re operational imperatives that dictate whether data becomes a liability or a strategic weapon.
The stakes are higher than ever. Regulatory frameworks like GDPR and CCPA impose strict penalties for non-compliance, while cyber threats evolve at a pace that outstrips legacy systems. Meanwhile, the explosion of unstructured data—from IoT sensors to customer interactions—demands frameworks that can classify, secure, and repurpose information dynamically. The answer lies in DLM, a methodology that ensures data remains accurate, accessible, and actionable throughout its lifecycle. But what exactly are the three foundational goals that underpin this methodology? And how do they translate into tangible outcomes for businesses?
Contrary to misconceptions, DLM isn’t merely about storage or backup—it’s a holistic strategy that balances utility, security, and compliance in a way that adapts to organizational needs. The first goal centers on preserving data integrity, ensuring that every record remains reliable from inception to archival. The second prioritizes minimizing risk exposure, whether through encryption, access controls, or automated purging of obsolete data. The third—often overlooked—focuses on maximizing operational efficiency, turning data into a self-sustaining resource rather than a passive archive. Together, these objectives form the bedrock of a system where data isn’t just managed, but optimized.
The Complete Overview of Data Lifecycle Management (DLM)
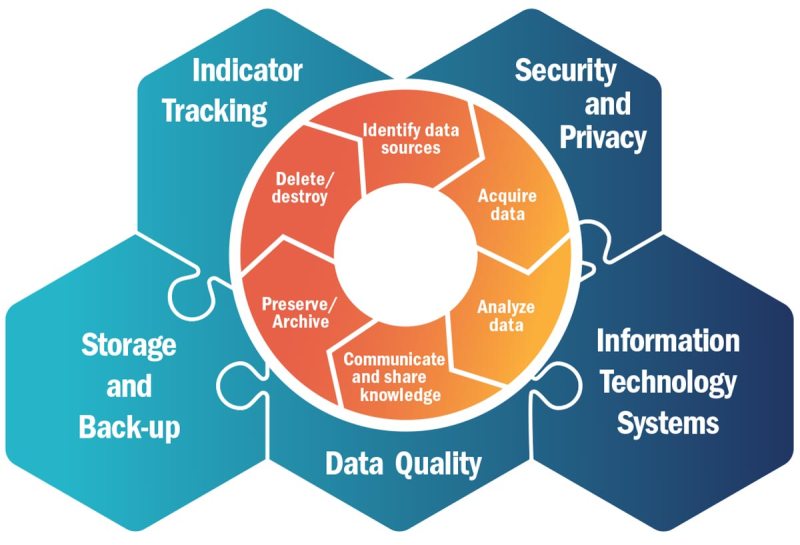
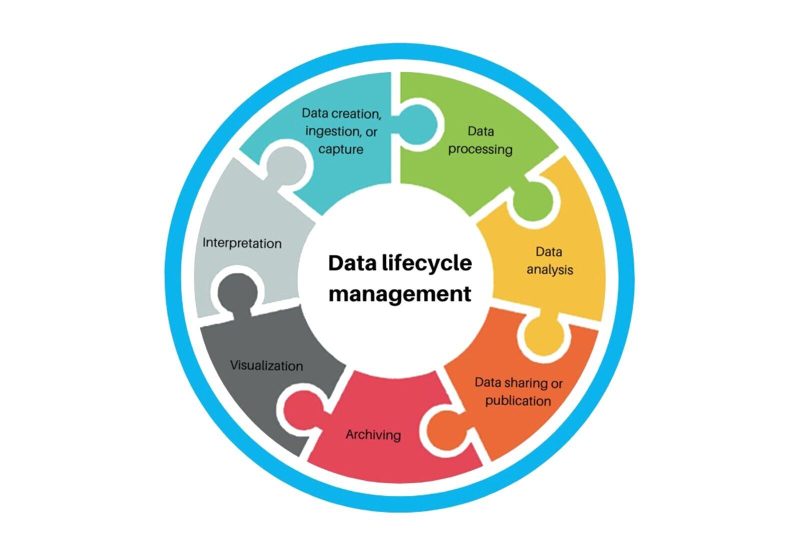
Data lifecycle management (DLM) is the systematic approach to overseeing data from its creation to its eventual disposal, encompassing stages like acquisition, processing, storage, usage, archiving, and deletion. At its core, DLM addresses a fundamental paradox: organizations generate more data than ever, yet only a fraction is actively used or properly governed. The gap between data volume and value is where DLM intervenes, ensuring that each phase of the lifecycle aligns with business objectives. What are the three main goals of DLM? They are not arbitrary targets but strategic priorities that resolve this paradox by enforcing consistency, security, and scalability.
The methodology’s power lies in its adaptability. A financial services firm, for instance, must adhere to strict retention policies for audit trails, while a retail chain prioritizes real-time analytics for inventory optimization. DLM frameworks like those from IBM, Microsoft, or open-source tools such as Apache Atlas provide modular solutions, allowing businesses to tailor policies to their specific needs. The key differentiator is that DLM treats data as a dynamic asset, not a static repository. This shift from reactive to proactive management is what separates high-performing organizations from those drowning in data inefficiencies.
Historical Background and Evolution
The origins of DLM trace back to the 1980s, when early database management systems (DBMS) introduced rudimentary lifecycle concepts like backup and recovery. However, it wasn’t until the 2000s—with the rise of big data and cloud computing—that DLM evolved into a specialized discipline. The turning point came with regulatory mandates: the Sarbanes-Oxley Act (2002) forced corporations to document financial data trails, while GDPR (2018) imposed stringent data protection requirements. These laws didn’t just create compliance obligations; they exposed the fragility of ad-hoc data management.
Table of Contents
- The Complete Overview of Data Lifecycle Management (DLM)
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does DLM differ from traditional data backup solutions?
- Q: Can small businesses benefit from DLM, or is it only for enterprises?
- Q: What role does AI play in modern DLM?
- Q: How often should data retention policies be reviewed?
- Q: What are the most common DLM failures, and how to avoid them?
- Q: Can DLM improve customer trust?
Today, DLM is shaped by three evolutionary forces. First, the digital transformation wave has decentralized data storage, with employees and third parties generating data across cloud platforms, edge devices, and hybrid environments. Second, cybersecurity threats—such as ransomware and insider breaches—have made data resilience a boardroom priority. Third, the democratization of data (via tools like Power BI or Tableau) has increased demand for self-service analytics, requiring DLM to balance governance with accessibility. The result is a modern framework that integrates automation, AI-driven classification, and policy-as-code to enforce consistency at scale.
Core Mechanisms: How It Works
DLM operates through a series of interconnected phases, each with distinct mechanisms to achieve its goals. The lifecycle begins with data ingestion, where raw inputs are validated for completeness and accuracy. This stage often employs metadata tagging to classify data by type (e.g., PII, financial records) and sensitivity level. The next phase, processing and storage, involves structuring data for query efficiency—whether through relational databases, data lakes, or object storage—and applying encryption or tokenization to protect sensitive fields. Automated workflows then route data to its designated endpoint, whether for active use, archival, or deletion.
The final phases—archiving and disposal—are where DLM’s goals converge. Archiving ensures long-term retention while optimizing storage costs (e.g., via cold storage tiers), while disposal adheres to legal or business policies (e.g., purging outdated customer records after 7 years). Critical to this process is auditability: DLM systems log every action, from access requests to deletion events, to satisfy compliance requirements. Tools like IBM’s InfoSphere or Collibra integrate with enterprise resource planning (ERP) and customer relationship management (CRM) systems to create a unified view of data flows, ensuring no phase is left ungoverned.
Key Benefits and Crucial Impact
Organizations that implement DLM don’t just mitigate risks—they unlock strategic advantages. The most immediate impact is cost reduction: studies show that poor data quality costs businesses up to 30% of revenue, while DLM automates cleanup and reduces redundant storage. Beyond savings, DLM enhances decision-making by ensuring data is timely, accurate, and contextually relevant. For example, a healthcare provider using DLM can trace patient records across systems, reducing errors in treatment plans. The third pillar is regulatory compliance, where automated retention policies and access controls eliminate manual oversight failures.
Yet the true transformative potential lies in innovation acceleration. When data is well-governed, teams can focus on analytics rather than data wrangling. A retail giant like Walmart, for instance, uses DLM to correlate point-of-sale data with supply chain logs, predicting demand with 95% accuracy. The bottom line? DLM isn’t a cost center—it’s an enabler of competitive differentiation. As what are the three main goals of DLM? suggest, the methodology’s value isn’t monolithic; it’s a multiplier effect across efficiency, security, and agility.
"Data governance isn’t about restrictions—it’s about unlocking the potential of your most valuable asset. The organizations that treat DLM as a strategic lever will outperform those clinging to siloed, reactive approaches."
— Gartner, 2023 Data & Analytics Summit
Major Advantages
- Risk Mitigation: Automated classification and encryption reduce exposure to breaches or legal penalties. For example, a breach involving unencrypted customer data under GDPR can incur fines up to 4% of global revenue.
- Operational Agility: Self-service data portals (enabled by DLM) let analysts query datasets without IT bottlenecks, cutting reporting cycles by up to 60%.
- Cost Efficiency: DLM slashes storage waste by identifying and purging obsolete data. One Fortune 500 company recovered $2.3M annually after implementing automated archival policies.
- Compliance Assurance: Built-in audit trails and retention policies automate adherence to laws like HIPAA or SOX, reducing manual audit workloads by 75%.
- Strategic Insights: Clean, well-documented data fuels AI/ML models. A DLM-optimized dataset improves predictive accuracy by 20–30% compared to ungoverned sources.

Comparative Analysis
| Traditional Data Management | Data Lifecycle Management (DLM) |
|---|---|
| Focuses on storage and backup; reactive to issues. | Proactive governance across all lifecycle stages; integrates security and compliance by design. |
| Manual processes for classification and retention. | Automated metadata tagging and policy enforcement (e.g., via AI-driven tools like Alation). |
| Silos data in departmental systems (e.g., HR, Finance). | Creates a unified data fabric with cross-system visibility (e.g., using data mesh architectures). |
| High operational costs due to redundant storage and manual audits. | Cost savings from automated cleanup, tiered storage, and reduced compliance fines. |
Future Trends and Innovations
The next frontier for DLM lies in autonomous governance. Emerging technologies like generative AI are poised to automate metadata tagging and even suggest retention policies based on contextual analysis. For instance, an AI could flag a contract as "high-risk" if it contains clauses violating GDPR, triggering automated redaction. Meanwhile, quantum-resistant encryption will become standard as post-quantum threats loom, ensuring data remains secure even against future decryption methods. Another trend is real-time DLM, where edge computing processes data at the source (e.g., IoT sensors) before it enters central repositories, reducing latency and bandwidth costs.
Regulatory evolution will also reshape DLM. The EU’s proposed Data Act (2024) will mandate data sharing standards across industries, forcing organizations to adopt interoperable DLM frameworks. Similarly, the rise of data sovereignty laws (e.g., China’s Personal Information Protection Law) will require DLM systems to enforce geofenced storage and processing rules. The overarching theme? DLM is shifting from a compliance checkbox to a competitive moat, with the most innovative firms embedding it into their digital DNA.
Conclusion
The question what are the three main goals of data lifecycle management (DLM)? isn’t just theoretical—it’s the compass for organizations navigating the data deluge. The first goal, integrity, ensures data is reliable; the second, security, protects it from threats; and the third, efficiency, maximizes its value. Together, they form a trifecta that transforms data from a passive byproduct into a dynamic force for growth. The companies that master DLM won’t just survive—they’ll thrive in an era where data is both a liability and a weapon.
Implementation begins with a clear strategy. Start by auditing existing data flows to identify gaps, then deploy tools that align with your goals (e.g., Collibra for governance, Cloudera for storage). Most critically, foster a culture where DLM isn’t an IT project but a business imperative. The data lifecycle isn’t linear—it’s a cycle of continuous improvement. And in that cycle, the three goals of DLM are the gears that keep it turning.
Comprehensive FAQs
Q: How does DLM differ from traditional data backup solutions?
A: Traditional backup focuses solely on recovery after data loss, while DLM governs data throughout its entire lifecycle, including creation, usage, archival, and secure disposal. Backup tools lack mechanisms for classification, retention policies, or compliance automation—key components of DLM.
Q: Can small businesses benefit from DLM, or is it only for enterprises?
A: DLM’s principles scale to any organization. Small businesses can start with lightweight tools like Google Drive’s retention policies or open-source solutions like Apache Atlas. The core goals—integrity, security, efficiency—apply universally, though the complexity of implementation varies by data volume.
Q: What role does AI play in modern DLM?
A: AI enhances DLM by automating classification (e.g., identifying PII), anomaly detection (flagging unusual access patterns), and policy suggestions (recommending retention periods). Tools like Microsoft Purview use AI to analyze data lineage and suggest governance actions, reducing manual effort by up to 80%.
Q: How often should data retention policies be reviewed?
A: Policies should be reviewed annually or whenever regulatory changes occur (e.g., new GDPR interpretations). Dynamic industries (e.g., fintech) may require quarterly reviews to adapt to evolving threats or business models. Automated DLM platforms can trigger alerts when policies become outdated.
Q: What are the most common DLM failures, and how to avoid them?
A: Failures typically stem from lack of stakeholder buy-in, overly rigid policies, or neglecting metadata management. To avoid them: (1) Involve legal, IT, and business teams in policy design; (2) Use flexible frameworks (e.g., data mesh) to adapt to change; (3) Invest in metadata tools (e.g., Alation) to maintain context across data silos.
Q: Can DLM improve customer trust?
A: Absolutely. DLM demonstrates transparency by ensuring data is handled ethically—e.g., via right-to-erasure compliance or bias mitigation in AI models. A 2023 study found that 68% of consumers trust brands more when they disclose data practices clearly, a direct outcome of robust DLM.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.