How Firewall Protection Addresses Modern Security in 2024
The cybersecurity landscape has evolved beyond simple antivirus software. Modern threats—ranging from state-sponsored attacks to AI-driven exploits—demand layered defenses, with firewall protection at the core of addressing contemporary security challenges. Unlike static perimeter defenses of the past, today’s firewalls integrate behavioral analysis, real-time threat intelligence, and adaptive policies to neutralize sophisticated intrusions before they breach critical systems.
What distinguishes firewall protection in 2024 is its ability to dynamically respond to evolving attack vectors. Traditional firewalls relied on rigid rule sets and IP-based filtering, but modern architectures leverage machine learning to detect anomalies in traffic patterns, block zero-day exploits, and enforce granular access controls. This shift reflects a broader paradigm: security is no longer a static barrier but an active, intelligence-driven process.
The question is no longer whether an organization needs firewall protection to address modern security, but how to deploy it effectively. With ransomware attacks surging by 93% in 2023 and cloud migrations exposing new attack surfaces, the stakes have never been higher. Below, we dissect the mechanics, advantages, and future of firewalls in safeguarding digital assets.
The Complete Overview of Firewall Protection Addressing Modern Security
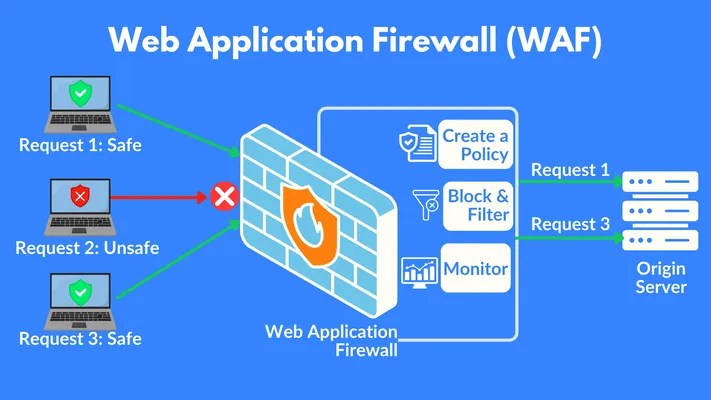
Firewall protection addressing modern security is a multi-layered strategy that combines traditional packet inspection with next-generation capabilities like deep packet inspection (DPI), sandboxing, and integration with SIEM (Security Information and Event Management) systems. The goal is to create a dynamic shield that adapts to the tactics of cyber adversaries, who increasingly exploit human error, unpatched vulnerabilities, and misconfigured cloud environments.At its essence, firewall protection today is about context-aware enforcement. Instead of merely filtering traffic based on predefined rules, modern firewalls analyze user behavior, device posture, and application-layer data to determine legitimacy. This contextual approach is critical in environments where employees access corporate networks via BYOD (Bring Your Own Device) policies or remote work setups, where traditional perimeter defenses fail.
Historical Background and Evolution
The concept of firewalls dates back to the late 1980s, when organizations first sought to isolate internal networks from the nascent internet. Early firewalls used packet filtering to block or allow traffic based on IP addresses and ports—a rudimentary but effective measure against the threats of the time. By the 1990s, stateful inspection firewalls emerged, tracking the state of active connections to prevent IP spoofing and other basic attacks.The turn of the millennium introduced firewall protection as a more sophisticated tool with the rise of deep packet inspection (DPI), which scrutinized the actual content of data packets. However, the real inflection point came with the proliferation of cloud computing and the Internet of Things (IoT). As networks became more distributed and heterogeneous, static firewalls proved inadequate. This led to the development of next-generation firewalls (NGFWs), which incorporated intrusion prevention systems (IPS), application awareness, and integration with threat intelligence feeds.
Core Mechanisms: How It Works
Modern firewalls operate on three primary layers: network, transport, and application. At the network layer, they filter traffic based on source/destination IP addresses and ports, a function inherited from their predecessors. The transport layer adds context by examining session states—whether a packet belongs to an established connection or is part of a new, potentially malicious attempt.Table of Contents
- The Complete Overview of Firewall Protection Addressing Modern Security
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does a next-generation firewall differ from a traditional firewall?
- Q: Can firewalls protect against zero-day vulnerabilities?
- Q: Are cloud-based firewalls as effective as on-premises firewalls?
- Q: How often should firewall rules be updated?
- Q: What is the role of firewalls in a zero-trust security model?
- Q: Can small businesses benefit from next-generation firewalls?
The most critical innovation lies in the application layer, where firewalls inspect payloads for malicious payloads, such as malware or command-and-control (C2) traffic. Advanced systems use behavioral analysis to detect deviations from normal traffic patterns, such as an employee suddenly downloading terabytes of data or a server communicating with a known command-and-control server. This is where firewall protection addresses modern security most effectively: by combining signature-based detection with anomaly-based monitoring.
Key Benefits and Crucial Impact
The adoption of firewall protection to address modern security is driven by its ability to mitigate risks across multiple vectors. From preventing data exfiltration to blocking lateral movement by attackers, firewalls serve as the first line of defense in a zero-trust architecture. They reduce the attack surface by enforcing least-privilege access, ensuring that even if an attacker bypasses one layer, they encounter additional barriers.The financial and operational impact is equally significant. According to IBM’s Cost of a Data Breach Report 2023, organizations with robust firewall protections experienced a 30% lower average breach cost compared to those without. Beyond cost savings, firewalls enhance compliance with regulations like GDPR, HIPAA, and PCI DSS by enforcing granular access controls and logging all suspicious activities.
"A firewall is no longer a static gatekeeper but a sentient guardian—one that learns, adapts, and evolves alongside the threat landscape." — Gartner, 2023 Cybersecurity Trends Report
Major Advantages
- Real-Time Threat Detection: AI-driven firewalls analyze traffic in real time, using threat intelligence feeds to block known malicious IPs, domains, and file hashes before they reach internal systems.
- Granular Access Control: Role-based policies and device posture checks ensure only authorized users and compliant devices access sensitive resources, reducing insider threats and credential abuse.
- Integration with Zero-Trust Frameworks: Modern firewalls align with zero-trust principles by verifying every access request, regardless of its origin, and enforcing continuous authentication.
- Scalability for Hybrid Environments: Cloud-native firewalls extend protection to SaaS applications, remote workers, and multi-cloud deployments, ensuring consistent security policies across diverse infrastructures.
- Automated Incident Response: Advanced firewalls can automatically quarantine infected endpoints, revoke compromised credentials, and trigger alerts for SOC (Security Operations Center) teams, reducing mean time to resolution (MTTR).

Comparative Analysis
| Traditional Firewalls | Next-Generation Firewalls (NGFWs) |
|---|---|
| Rule-based filtering (IP/port) | AI-driven behavioral analysis + threat intelligence |
| Limited to network/transport layers | Full application-layer inspection (DPI) |
| Static policies, manual updates | Automated policy adjustments via ML |
| Perimeter-focused defense | Zero-trust integration, identity-aware protection |
Future Trends and Innovations
The next frontier for firewall protection addressing modern security lies in quantum-resistant encryption and AI-driven predictive analytics. As quantum computing threatens to break current cryptographic standards, firewalls will incorporate post-quantum algorithms to safeguard data in transit. Simultaneously, predictive AI will shift from reactive blocking to proactive threat hunting, identifying vulnerabilities before they are exploited.Another emerging trend is the convergence of firewalls with extended detection and response (XDR) platforms. These integrated solutions correlate data across endpoints, networks, and cloud environments, providing a holistic view of threats. Additionally, the rise of edge computing will demand lightweight, distributed firewalls capable of securing IoT devices and remote sensors without overwhelming central security teams.

Conclusion
The role of firewall protection in addressing modern security has transcended its origins as a simple traffic filter. Today, it is a cornerstone of proactive defense, blending traditional perimeter controls with cutting-edge technologies like AI, automation, and zero-trust principles. Organizations that fail to modernize their firewall strategies risk falling victim to increasingly sophisticated attacks.The key takeaway is clear: firewall protection is not a one-time implementation but an ongoing process of adaptation. As cyber threats grow in complexity, so too must the defenses. By leveraging next-generation firewalls, integrating them with broader security architectures, and staying ahead of emerging trends, businesses can turn the tide against cybercrime.
Comprehensive FAQs
Q: How does a next-generation firewall differ from a traditional firewall?
A: Traditional firewalls rely on static rules (e.g., IP/port blocking) and operate at the network/transport layers. Next-generation firewalls (NGFWs) incorporate deep packet inspection, application awareness, intrusion prevention, and AI-driven threat detection, operating across all OSI layers to provide context-aware security.
Q: Can firewalls protect against zero-day vulnerabilities?
A: While firewalls cannot block zero-days based on signatures alone, modern NGFWs use behavioral analysis and anomaly detection to identify suspicious activity patterns that may indicate a zero-day exploit. Integration with threat intelligence feeds further enhances detection capabilities.
Q: Are cloud-based firewalls as effective as on-premises firewalls?
A: Cloud-based firewalls offer scalability and real-time updates but may lack the granular control of on-premises solutions in hybrid environments. The best approach is a unified firewall strategy that combines cloud-native protections with on-premises enforcement for critical assets.
Q: How often should firewall rules be updated?
A: Firewall rules should be reviewed and updated at least quarterly, or immediately after detecting new threats. Automated systems with threat intelligence feeds can reduce manual updates, but human oversight remains essential for policy refinement.
Q: What is the role of firewalls in a zero-trust security model?
A: In zero-trust, firewalls enforce least-privilege access by verifying every request based on identity, device health, and contextual factors (e.g., location, time). They act as a critical component of micro-segmentation, ensuring lateral movement is restricted even if an attacker gains initial access.
Q: Can small businesses benefit from next-generation firewalls?
A: Absolutely. While large enterprises face more complex threats, SMBs are increasingly targeted due to perceived weaker defenses. NGFWs offer affordable, scalable protection with features like automated threat blocking and compliance reporting, making them ideal for businesses of all sizes.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.