What Are RSA? The Cryptographic Powerhouse Behind Secure Transactions
When you log into your bank account, send encrypted emails, or verify a software download, you’re likely interacting with what are RSA—the cryptographic backbone of modern security. Unlike symmetric encryption, which relies on a single shared key, RSA leverages asymmetric mathematics: two mathematically linked keys (public and private) that enable secure communication without prior key exchange. This dual-key system isn’t just theoretical; it’s the reason your credit card details remain confidential during online purchases and why governments trust it for classified communications.
The acronym RSA stands for Rivest-Shamir-Adleman, named after the MIT researchers who published it in 1977. What makes it revolutionary isn’t just its complexity but its elegance: a 2048-bit RSA key can resist brute-force attacks for centuries, yet it’s computationally efficient enough to power everyday devices. From SSL/TLS certificates to Bitcoin’s blockchain, RSA’s influence is invisible yet ubiquitous—proving that the most powerful technologies often operate silently in the background.
Yet despite its ubiquity, what are RSA remains misunderstood. Many associate it with "unbreakable encryption," but its security hinges on mathematical assumptions (like the difficulty of factoring large primes) that could one day falter. Others conflate it with digital signatures, ignoring that RSA’s true genius lies in its dual-purpose design: encrypting data and verifying identities. To truly grasp its role, we must dissect its origins, mechanics, and the quiet battles shaping its future.

The Complete Overview of RSA Cryptography
At its core, what are RSA refers to an asymmetric encryption algorithm that transforms plaintext into ciphertext using a public key, then decrypts it with a private key—or vice versa for digital signatures. Unlike older methods like Caesar ciphers, RSA’s security derives from the computational infeasibility of reversing its operations without the corresponding key. This asymmetry eliminates the need for secure key distribution, a major bottleneck in classical cryptography. Today, RSA is the de facto standard for securing communications, authentication, and data integrity across industries, from healthcare to fintech.The algorithm’s foundation rests on two mathematical pillars: modular arithmetic and prime factorization. When you generate an RSA key pair, the system selects two large prime numbers, combines them into a modulus (n), and derives exponents (e and d) that are inverses modulo φ(n). The public key (n, e) can be shared openly, while the private key (n, d) remains secret. This structure ensures that even if an attacker intercepts encrypted data, reconstructing the original message without the private key is equivalent to solving a problem that would take a supercomputer millennia.
Historical Background and Evolution
RSA’s origins trace back to 1973, when Whitfield Diffie and Martin Hellman proposed public-key cryptography in their seminal paper, "New Directions in Cryptography." Their work inspired Ron Rivest, Adi Shamir, and Leonard Adleman to formalize the first practical implementation—RSA—in 1977. What they didn’t anticipate was the algorithm’s immediate adoption by governments and corporations. By the 1990s, what are RSA had become the cornerstone of the emerging internet, enabling secure email (PGP) and early e-commerce protocols.The algorithm’s longevity stems from its adaptability. In 1991, RSA Security Inc. commercialized it as a product, licensing it to companies like Microsoft and Netscape. The 1994 introduction of SSL (precursor to TLS) cemented RSA’s role in web security, while the 2000s saw its integration into cryptographic standards like PKCS#1. Even today, despite quantum computing threats, RSA endures through hybrid systems (combining it with elliptic curve cryptography) and post-quantum research. Its evolution mirrors the digital age itself: a tool that grew from academic curiosity into an invisible shield for global infrastructure.
Core Mechanisms: How It Works
RSA’s magic lies in its reliance on prime number factorization, a problem that grows exponentially harder as numbers increase. To encrypt a message, the sender uses the recipient’s public key (e, n) to compute ciphertext via modular exponentiation: `c = m^e mod n`. Decryption reverses this with the private key (d, n): `m = c^d mod n`. The security assumption? That no efficient algorithm exists to factor n into its primes p and q, which would reveal d. This is why RSA keys are measured in bits (e.g., 2048-bit keys use primes ~600 digits long).Table of Contents
- The Complete Overview of RSA Cryptography
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How does RSA encryption differ from symmetric encryption?
- Q: Can RSA be broken? If so, how?
- Q: Why do websites use RSA for SSL/TLS if it’s slow?
- Q: How do I generate an RSA key pair?
- Q: What’s the difference between RSA encryption and RSA signatures?
- Q: Are there any real-world examples of RSA failures?
- Q: How does RSA relate to Bitcoin?
- Q: What’s the largest RSA key ever factored?
- Q: Can I use RSA for password hashing?
- Q: How does RSA handle large files?
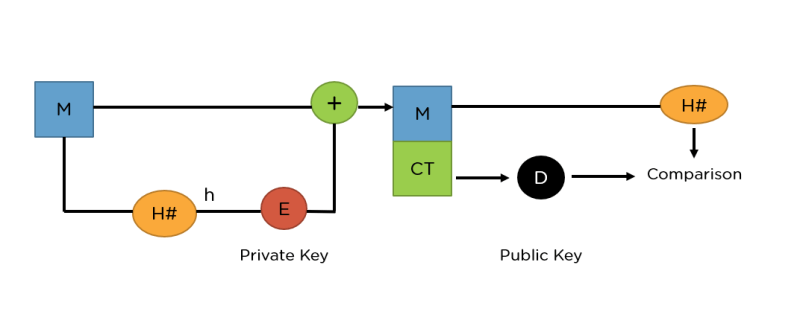
The algorithm’s dual functionality extends beyond encryption. For digital signatures, the sender "signs" a message with their private key, and the recipient verifies it using the sender’s public key. This non-repudiation feature is critical for contracts, code signing, and blockchain transactions. However, RSA’s computational overhead—especially for large keys—has led to optimizations like OAEP padding (for encryption) and PSS padding (for signatures), which mitigate vulnerabilities like chosen-ciphertext attacks.
Key Benefits and Crucial Impact
Few cryptographic systems have achieved RSA’s blend of theoretical rigor and real-world utility. Its asymmetric design solves the "key distribution problem," allowing strangers to exchange secrets without prior coordination. This property underpins what are RSA’s dominance in authentication: SSL/TLS certificates, code signing, and even Bitcoin’s address generation rely on RSA’s ability to bind identities to keys. Governments use it for classified communications (e.g., the U.S. Digital Signature Standard), while individuals depend on it daily for password resets and secure logins.The algorithm’s impact transcends technology. By enabling trust in digital transactions, RSA has reshaped economies—e-commerce, online banking, and IoT devices all depend on its integrity. Yet its influence isn’t just economic; it’s cultural. RSA’s adoption in tools like GPG (for privacy activists) and Let’s Encrypt (for free SSL certificates) democratized security, proving that cryptography could be both powerful and accessible. As one cryptographer noted:
"RSA didn’t just secure the internet; it redefined what ‘secure’ means in a connected world. Its elegance lies in the fact that it turned abstract math into a practical shield—one that could be deployed anywhere, by anyone." — Dr. Mihir Bellare, Cryptographer & UCLA Professor
Major Advantages
- Asymmetric Security: Eliminates the need for pre-shared secrets, enabling secure communication between parties with no prior relationship.
- Versatility: Supports both encryption and digital signatures, making it suitable for authentication, non-repudiation, and data integrity.
- Proven Track Record: Decades of cryptanalysis have failed to break well-implemented RSA, though key sizes must scale with computational power.
- Standardization: Widely adopted in protocols like TLS, SSH, and S/MIME, ensuring interoperability across systems.
- Key Management Simplicity: Public keys can be freely distributed, reducing the risk of key compromise during transmission.

Comparative Analysis
While RSA remains dominant, alternatives like Elliptic Curve Cryptography (ECC) and Diffie-Hellman offer trade-offs in speed and key size. Below is a direct comparison:| Feature | RSA | ECC |
|---|---|---|
| Key Size (Equivalent Security) | 2048-bit | 256-bit |
| Computational Efficiency | Slower (due to large exponents) | Faster (smaller key operations) |
| Use Cases | Encryption, signatures, TLS | Signatures, key exchange (ECDHE) |
| Quantum Vulnerability | High (Shor’s algorithm) | High (but larger keys mitigate risk) |
Future Trends and Innovations
RSA’s future hinges on two existential threats: quantum computing and side-channel attacks. Shor’s algorithm could render RSA obsolete by factoring large primes efficiently, prompting a shift to post-quantum cryptography (e.g., lattice-based schemes). Meanwhile, advances in lattice cryptography (like Kyber and Dilithium) are already being standardized by NIST. Yet RSA isn’t disappearing—it’s evolving. Hybrid encryption (combining RSA with post-quantum algorithms) and deterministic RSA (for signature efficiency) are bridging the gap.Another frontier is homomorphic encryption, where RSA-like structures enable computations on encrypted data without decryption. Projects like Microsoft’s SEAL and IBM’s HomomorphicEncryption.org are exploring this, though practical deployment remains years away. For now, RSA’s role in zero-trust architectures and decentralized identity (e.g., self-sovereign IDs) ensures its relevance. The question isn’t whether RSA will fade, but how it will adapt to a world where its mathematical foundations are no longer invincible.
Conclusion
What are RSA is more than an algorithm—it’s a testament to how abstract mathematics can become the bedrock of trust in a digital age. From its 1977 inception to today’s quantum-resistant research, RSA has weathered cryptographic revolutions by remaining adaptable. Its legacy isn’t just in securing transactions but in proving that cryptography could be both robust and scalable. Yet its story isn’t over. As quantum threats loom, RSA’s next chapter may involve a symbiotic relationship with emerging paradigms, ensuring that the principles of asymmetric cryptography endure long after its original form retires.The lesson of RSA is clear: security isn’t static. It’s a dynamic interplay of theory, implementation, and foresight. Whether you’re a developer, policymaker, or everyday user, understanding what are RSA isn’t just about grasping an encryption method—it’s about recognizing the invisible infrastructure that keeps the digital world functional.
Comprehensive FAQs
Q: How does RSA encryption differ from symmetric encryption?
A: RSA uses a public-private key pair, allowing encryption with one key and decryption with another. Symmetric encryption (e.g., AES) uses a single shared key for both operations, requiring secure key exchange beforehand. RSA’s asymmetry eliminates this need but is computationally heavier.
Q: Can RSA be broken? If so, how?
A: RSA’s security relies on the difficulty of factoring large primes. Classical attacks (e.g., Pollard’s rho) are impractical for well-sized keys (2048+ bits). However, quantum computers using Shor’s algorithm could factor large numbers efficiently, breaking RSA. Post-quantum alternatives are already being developed to counter this.
Q: Why do websites use RSA for SSL/TLS if it’s slow?
A: RSA’s primary role in TLS is key exchange (via RSA key transport) or digital signatures (for certificates). While RSA encryption itself is slow, it’s often used to establish a symmetric session key (e.g., AES) for faster data transfer. Modern TLS prefers ECDHE for key exchange due to efficiency, but RSA remains critical for backward compatibility and certificate validation.
Q: How do I generate an RSA key pair?
A: Using OpenSSL, run:
openssl genpkey -algorithm RSA -out private_key.pem -pkeyopt rsa_keygen_bits:2048
The private key (`private_key.pem`) is kept secret, while the public key is derived from it (e.g., via `openssl rsa -pubout`). Never share the private key—it grants full control over the key pair.
Q: What’s the difference between RSA encryption and RSA signatures?
A: RSA Encryption uses the recipient’s public key to encrypt data, which only the recipient’s private key can decrypt. RSA Signatures use the sender’s private key to "sign" data, and the recipient verifies it with the sender’s public key. Signatures prove authenticity and integrity, while encryption ensures confidentiality.
Q: Are there any real-world examples of RSA failures?
A: Yes. In 2017, the WannaCry ransomware exploited a flaw in RSA-implemented SMB protocols (not RSA itself). Another case involved RSA SecurID tokens, where poor random number generation in early implementations allowed brute-force attacks. These failures highlight the importance of proper key generation and padding schemes (e.g., OAEP).
Q: How does RSA relate to Bitcoin?
A: Bitcoin uses ECDSA (Elliptic Curve Digital Signature Algorithm) for transactions, but RSA’s influence is indirect. Bitcoin addresses are derived from public keys (often using secp256k1, an ECC variant), and RSA-like principles underpin the cryptographic proofs ensuring transaction validity. RSA’s legacy in digital signatures inspired Bitcoin’s reliance on asymmetric cryptography for trustless verification.
Q: What’s the largest RSA key ever factored?
A: As of 2023, the largest RSA key factored is RSA-240 (795 bits), achieved by a distributed computing project in 2019. Factoring RSA-2048 would require trillions of years with current technology, but quantum advancements could change this. The record demonstrates why key sizes must grow over time.
Q: Can I use RSA for password hashing?
A: No. RSA is designed for encryption/signatures, not hashing. Passwords should use slow hash functions (e.g., bcrypt, Argon2) with salt to resist brute-force attacks. RSA’s deterministic nature makes it unsuitable for hashing, where uniqueness and irreversibility are critical.
Q: How does RSA handle large files?
A: RSA is inefficient for large files due to its computational overhead. Instead, files are encrypted with a symmetric key (e.g., AES), which is then encrypted with RSA. This hybrid approach (e.g., PGP) combines RSA’s secure key exchange with symmetric encryption’s speed.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.