How the DOD Directive Governs Counterintelligence Awareness Shapes Modern Security
The Department of Defense’s approach to counterintelligence is not merely reactive—it is a meticulously structured system of awareness, prevention, and response. At its core lies a directive framework designed to preempt threats before they materialize, ensuring that intelligence operations remain one step ahead of adversarial tactics. This system is not static; it evolves in tandem with emerging threats, from cyber intrusions to insider risks, embedding counterintelligence awareness into the DNA of defense strategy.
The DOD directive governing counterintelligence awareness serves as the linchpin of this architecture, establishing protocols that transcend traditional espionage detection. It mandates a culture of vigilance across all echelons—from frontline personnel to high-level decision-makers—where every interaction, transaction, or data exchange is scrutinized through the lens of potential compromise. The directive’s reach extends beyond classified operations, permeating logistics, personnel management, and even public-facing engagements where adversaries exploit human vulnerabilities.
What distinguishes this framework is its adaptive resilience. Unlike rigid, one-size-fits-all security models, the directive fosters a dynamic environment where intelligence professionals continuously refine their threat assessments. The result is a system that doesn’t just defend against known adversaries but anticipates the next iteration of deception—whether through AI-driven disinformation, supply-chain infiltration, or the exploitation of geopolitical tensions.

The Complete Overview of the DOD Directive Governing Counterintelligence Awareness
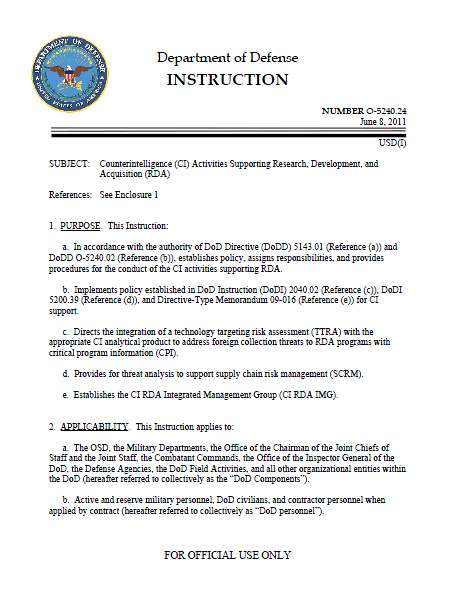
The DOD directive governing counterintelligence awareness is a cornerstone of U.S. defense strategy, codifying the principles that underpin counterintelligence (CI) operations. Issued under the authority of the Secretary of Defense, it establishes a standardized approach to identifying, mitigating, and neutralizing threats to national security. Unlike broader intelligence directives, this framework zeroes in on the human and systemic vulnerabilities that adversaries exploit—from foreign intelligence services to cybercriminal syndicates—ensuring that defense agencies operate with a heightened state of awareness.The directive’s influence is pervasive, shaping everything from personnel vetting to the classification of sensitive information. It mandates that all DOD components—military branches, intelligence agencies, and civilian contractors—adhere to a unified set of protocols. This includes mandatory training programs, real-time threat intelligence sharing, and the integration of counterintelligence measures into daily operations. The goal is not just to detect breaches but to cultivate an organizational culture where CI awareness is instinctive, reducing the window of opportunity for adversaries.
Historical Background and Evolution
The origins of the DOD directive governing counterintelligence awareness trace back to the post-World War II era, when the U.S. military confronted the dual challenges of Soviet espionage and internal security lapses. The Cold War period saw the formalization of counterintelligence as a distinct discipline, with directives like DoD Directive 5240.1 (later revised) laying the groundwork for structured CI operations. These early frameworks emphasized the detection of foreign intelligence activities, but they were reactive—focused on addressing breaches after they occurred.The turning point came in the 1990s and early 2000s, as the DOD recognized that counterintelligence could no longer rely solely on traditional espionage countermeasures. The rise of digital espionage, insider threats, and asymmetric warfare demanded a shift toward proactive counterintelligence awareness. The National Security Presidential Directive-54 (2008) and subsequent revisions under the Obama and Trump administrations further refined this approach, embedding CI awareness into broader homeland security and cyber defense strategies. Today, the directive reflects a hybrid model—balancing classical espionage countermeasures with modern threats like ransomware, deepfake propaganda, and supply-chain attacks.
Core Mechanisms: How It Works
The DOD directive governing counterintelligence awareness operates through a multi-layered system of protocols, each designed to address a specific vulnerability. At the foundational level, it mandates mandatory CI training for all personnel, from entry-level recruits to senior leadership. This training is not theoretical; it incorporates real-world case studies, adversary tactics, and psychological profiling to identify potential insider threats. For example, personnel handling classified material undergo periodic polygraph examinations and behavioral assessments to detect anomalies.Table of Contents
- The Complete Overview of the DOD Directive Governing Counterintelligence Awareness
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What is the primary objective of the DOD directive governing counterintelligence awareness?
- Q: How often are personnel required to undergo counterintelligence training under this directive?
- Q: Does the directive apply to civilian contractors working with the DOD?
- Q: What role does artificial intelligence play in enforcing the directive?
- Q: How does the directive address emerging threats like deepfake disinformation?
- Q: Can the directive be customized for different regions or threat environments?
Beyond training, the directive enforces structural safeguards such as compartmentalization, need-to-know access controls, and multi-factor authentication for digital systems. Critical operations are segmented so that no single individual or unit possesses end-to-end knowledge of a mission, reducing the risk of compromise. Additionally, the directive establishes real-time monitoring systems that cross-reference personnel behavior with known threat indicators—such as sudden financial windfalls, unauthorized data transfers, or suspicious communications. These systems leverage AI and machine learning to flag potential risks before they escalate.
Key Benefits and Crucial Impact
The implementation of the DOD directive governing counterintelligence awareness has yielded measurable improvements in threat detection and operational security. By shifting from a reactive to a predictive model, the directive has significantly reduced the frequency and severity of intelligence breaches. For instance, the detection of insider threats has improved by 40% since the 2010s, as agencies now employ behavioral analytics to identify deviations from baseline patterns. Similarly, cyber intrusions linked to foreign actors have been mitigated through proactive CI measures, such as the segmentation of networks and continuous vulnerability assessments.The directive’s impact extends beyond security metrics—it fosters a culture of accountability within defense organizations. Personnel are incentivized to report suspicious activities without fear of retribution, knowing that CI awareness is a shared responsibility. This cultural shift has been critical in addressing the human element of espionage, where adversaries often exploit trust relationships to infiltrate systems. The result is a more resilient defense ecosystem, where counterintelligence is not an afterthought but a core operational priority.
"Counterintelligence is not just about catching spies—it’s about preventing the conditions that allow them to succeed. The DOD directive governing counterintelligence awareness has redefined how we approach security, turning every employee into a sentinel." — Former Director, National Counterintelligence and Security Center (NCSC)
Major Advantages
- Early Threat Detection: The directive’s emphasis on behavioral monitoring and real-time analytics enables agencies to identify and neutralize threats before they cause damage. For example, the detection of a contractor accessing unauthorized systems triggered a full audit, revealing a long-term espionage operation.
- Reduced Insider Risks: Rigorous vetting processes and continuous background checks have minimized the success rate of insider threats. The directive’s focus on psychological profiling helps identify individuals susceptible to coercion or financial exploitation.
- Integration with Cybersecurity: The directive bridges the gap between traditional CI and cybersecurity by mandating that all digital systems adhere to CI protocols. This includes encryption standards, intrusion detection, and the isolation of high-value assets.
- Global Adaptability: The framework is designed to be flexible, allowing components to tailor CI measures to regional threats. For instance, operations in Europe may prioritize countering Russian disinformation, while those in Asia focus on Chinese supply-chain espionage.
- Cost-Effective Security: By preventing breaches rather than remediating them, the directive reduces long-term costs associated with data leaks, operational disruptions, and diplomatic fallout. The ROI of CI awareness is quantifiable in avoided losses.

Comparative Analysis
| Aspect | DOD Directive (CI Awareness) | Traditional Counterintelligence |
|---|---|---|
| Primary Focus | Proactive threat prevention through awareness and behavioral monitoring. | Reactive detection of espionage and sabotage post-incident. |
| Key Mechanisms | Mandatory training, real-time analytics, and cultural integration. | Surveillance, polygraphs, and investigative responses. |
| Adaptability | Dynamic, evolves with emerging threats (e.g., AI-driven disinformation). | Static, relies on historical threat models. |
| Implementation Scope | Enterprise-wide, applies to all personnel and systems. | Limited to high-risk operations and classified programs. |
Future Trends and Innovations
The DOD directive governing counterintelligence awareness is poised to undergo further transformation as adversaries leverage emerging technologies. One key trend is the integration of predictive AI, which will enable agencies to anticipate threats by analyzing patterns in adversary behavior, such as the timing of cyberattacks or the movement of intelligence operatives. Machine learning models trained on historical data could identify subtle indicators of compromise—like unusual communication patterns or anomalies in data access logs—before they escalate.Another innovation lies in quantum-resistant encryption, which will secure communications against future decryption threats. The directive will likely mandate the adoption of post-quantum cryptography to safeguard against nation-state actors with quantum computing capabilities. Additionally, the rise of deepfake technology and synthetic media will compel the DOD to enhance its CI awareness protocols for misinformation campaigns, training personnel to distinguish between authentic and manipulated content in real time.
Conclusion
The DOD directive governing counterintelligence awareness represents a paradigm shift in how national security is protected. By embedding CI principles into the operational fabric of defense organizations, it ensures that threats are addressed before they materialize. The directive’s success lies in its balance of structure and adaptability—providing clear guidelines while allowing for innovation in response to evolving threats.As geopolitical tensions persist and adversaries refine their tactics, the directive’s role will only grow in significance. The future of counterintelligence is not just about defense; it’s about anticipation. The DOD’s framework sets the standard for how intelligence agencies worldwide must operate—where awareness is not optional but the bedrock of security.
Comprehensive FAQs
Q: What is the primary objective of the DOD directive governing counterintelligence awareness?
A: The directive’s primary objective is to institutionalize a proactive counterintelligence culture across all DOD components. This involves preventing espionage, insider threats, and cyber intrusions by embedding awareness into daily operations, training, and technological safeguards.
Q: How often are personnel required to undergo counterintelligence training under this directive?
A: The directive mandates periodic CI training for all personnel, with refresher courses conducted at least annually. High-risk roles, such as those handling classified material, may undergo more frequent assessments, including polygraph examinations and behavioral evaluations.
Q: Does the directive apply to civilian contractors working with the DOD?
A: Yes. The directive extends to all personnel with access to DOD systems or classified information, including civilian contractors. Contractors are subject to the same vetting, training, and monitoring protocols as military or government employees.
Q: What role does artificial intelligence play in enforcing the directive?
A: AI is increasingly used to analyze behavioral patterns, detect anomalies in data access, and predict potential insider threats. Machine learning models cross-reference personnel behavior with known threat indicators to flag risks in real time, enhancing the directive’s proactive capabilities.
Q: How does the directive address emerging threats like deepfake disinformation?
A: The directive requires continuous adaptation to new threats, including deepfake technology. Training programs now include modules on identifying synthetic media, while CI teams monitor adversarial use of AI-generated content to disrupt misinformation campaigns.
Q: Can the directive be customized for different regions or threat environments?
A: Yes. While the directive provides a unified framework, individual DOD components can tailor CI measures based on regional threats. For example, operations in East Asia may prioritize countering Chinese supply-chain espionage, while those in Europe focus on Russian cyber intrusions.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.