How to Secure Your Corporate Sign Password: The Definitive Guide
Corporate sign password systems are the unsung backbone of modern enterprise security—yet their complexity often leads to vulnerabilities. The wrong approach can leave sensitive data exposed, while the right implementation fortifies digital perimeters. This isn’t just about passwords; it’s about layered authentication, compliance, and future-readiness.
Many organizations treat sign password protocols as a checkbox rather than a strategic asset. The consequences? Data breaches, regulatory fines, and reputational damage. A well-structured sign password comprehensive guide corporate isn’t optional—it’s a necessity for risk mitigation.
The stakes are higher than ever. With remote work, third-party integrations, and AI-driven threats, traditional password policies are obsolete. This guide cuts through the noise, offering actionable insights for CISOs, IT directors, and security teams.
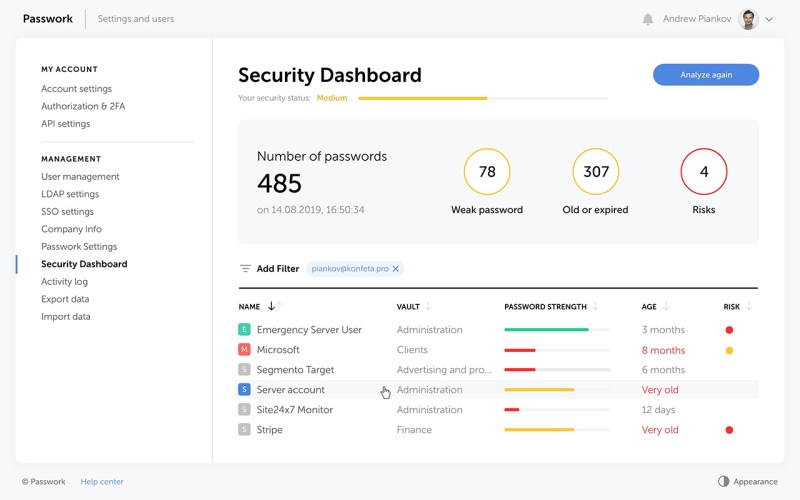
The Complete Overview of Corporate Sign Password Systems
Corporate sign password systems are the first line of defense in identity verification, governing access to critical systems, customer data, and internal networks. These systems have evolved from static credentials to multi-factor authentication (MFA) ecosystems, yet their core purpose remains unchanged: to authenticate users while minimizing unauthorized entry.The term "sign password comprehensive guide corporate" encompasses more than password policies—it includes biometric verification, behavioral analytics, and zero-trust frameworks. Modern implementations blend technical controls with user experience, balancing security without stifling productivity.
Historical Background and Evolution
Early corporate password systems relied on simple alphanumeric combinations, vulnerable to brute-force attacks. The 1990s introduced password complexity rules (e.g., special characters, length requirements), but these were quickly bypassed by credential stuffing. By the 2000s, enterprises adopted sign password comprehensive guide corporate principles like password rotation and single sign-on (SSO), reducing friction while improving security.Today, the landscape is dominated by identity and access management (IAM) platforms, which integrate with cloud services, mobile devices, and third-party applications. The shift from "password-only" to corporate sign password protocols with MFA and adaptive authentication marks a paradigm shift—one driven by regulatory demands (e.g., GDPR, HIPAA) and cyber threats.
Core Mechanisms: How It Works
At its core, a sign password comprehensive guide corporate system operates through three layers:1. Authentication: Verifying user identity via passwords, tokens, or biometrics.
2. Authorization: Granting access based on role-based permissions.
3. Audit Logging: Tracking all sign-in attempts for anomaly detection.
Table of Contents
- The Complete Overview of Corporate Sign Password Systems
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What’s the difference between a password policy and a corporate sign password system?
- Q: How often should corporate passwords be rotated?
- Q: Can AI improve corporate sign password security?
- Q: What’s the biggest misconception about corporate sign password systems?
- Q: How do third-party vendors fit into a corporate sign password strategy?
Modern implementations leverage corporate sign password management tools like Okta, Azure AD, or Ping Identity, which enforce policies dynamically. For example, a user accessing a high-risk system may trigger additional verification, while routine logins rely on cached credentials.
Key Benefits and Crucial Impact
A robust sign password comprehensive guide corporate framework reduces breach risks by 70% (Verizon DBIR). It also streamlines compliance with standards like ISO 27001 and NIST SP 800-63. Beyond security, it enhances user trust—employees and customers expect seamless, secure access.The ripple effects extend to operational efficiency. Automated password resets and SSO eliminate helpdesk bottlenecks, while adaptive policies reduce false positives in threat detection.
"Passwords are the weakest link in cybersecurity—but when paired with contextual authentication, they become a fortress." — Gartner, 2023 Identity Security Report
Major Advantages
- Reduced Credential Theft: MFA and behavioral analytics thwart phishing and credential stuffing.
- Compliance Alignment: Automates adherence to GDPR, SOX, and industry-specific regulations.
- Scalability: Cloud-based IAM adapts to remote teams and global expansions.
- Cost Savings: Fewer breaches mean lower incident response costs (avg. $4.45M per breach, IBM 2023).
- User Experience: SSO and passwordless options improve adoption rates.

Comparative Analysis
| Traditional Passwords | Modern Corporate Sign Password Systems |
|---|---|
| Static credentials, vulnerable to leaks. | Dynamic, context-aware authentication (e.g., device posture checks). |
| Manual password resets (high IT overhead). | Self-service recovery with MFA and AI-driven fraud detection. |
| No audit trails for access. | Real-time logging with SIEM integration for threat hunting. |
| Limited to on-premise systems. | Supports hybrid/multi-cloud environments with zero-trust principles. |
Future Trends and Innovations
The next decade will see corporate sign password management evolve toward passwordless authentication (e.g., FIDO2, WebAuthn) and AI-driven risk scoring. Biometric fusion (facial recognition + behavioral patterns) will reduce friction while enhancing security. Additionally, decentralized identity (DID) protocols may redefine how enterprises verify users without centralized databases.Regulatory pressures will accelerate these shifts, with frameworks like the EU’s eIDAS 2.0 mandating stronger authentication standards. Organizations must future-proof their sign password comprehensive guide corporate strategies today.

Conclusion
A well-architected sign password comprehensive guide corporate is non-negotiable in 2024. It’s not just about passwords—it’s about building a resilient identity ecosystem that balances security, compliance, and usability. The organizations that treat it as a strategic priority will outpace competitors in both risk mitigation and innovation.The time to act is now. Start by auditing your current corporate sign password protocols, then integrate MFA, SSO, and adaptive policies. The cost of inaction far outweighs the investment in a secure authentication framework.
Comprehensive FAQs
Q: What’s the difference between a password policy and a corporate sign password system?
A: A password policy sets rules (e.g., length, complexity), while a corporate sign password system includes authentication methods (MFA, biometrics), authorization logic, and audit trails. The latter is a holistic framework.
Q: How often should corporate passwords be rotated?
A: NIST now recommends against forced rotation unless breaches occur. Instead, enforce strong initial passwords and MFA. Rotation frequency depends on risk—high-security systems may require quarterly changes.
Q: Can AI improve corporate sign password security?
A: Yes. AI detects anomalies (e.g., unusual login locations) and automates password resets. Tools like Darktrace use behavioral AI to flag compromised accounts before breaches occur.
Q: What’s the biggest misconception about corporate sign password systems?
A: Many assume complexity equals security. Over-engineering (e.g., excessive MFA prompts) frustrates users, leading to workarounds. The goal is balance—security without sacrificing usability.
Q: How do third-party vendors fit into a corporate sign password strategy?
A: Vendors must adhere to your sign password comprehensive guide corporate standards via SAML/OAuth integrations. Conduct regular access reviews and enforce least-privilege principles for external partners.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.