How the AWS Console Transformed Cloud Infrastructure Management
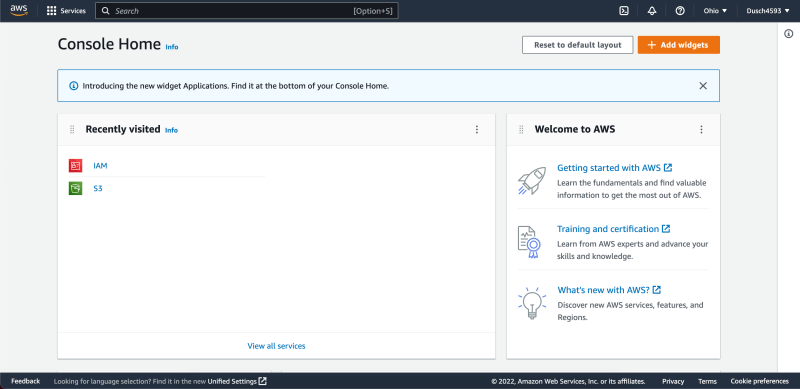
The AWS Console is not just another administrative tool—it’s the nervous system of Amazon Web Services, where developers, sysadmins, and enterprises orchestrate entire digital ecosystems. Behind its intuitive interface lies a sophisticated framework designed to balance scalability with granular control, enabling organizations to deploy, monitor, and optimize cloud resources without the friction of legacy systems. What makes the AWS Console uniquely powerful is its ability to abstract complexity while exposing the underlying infrastructure when needed, a duality that has redefined how businesses approach cloud adoption.
Yet, for all its capabilities, the AWS Console remains an evolving entity, shaped by decades of cloud computing advancements and the relentless demands of global enterprises. Its design reflects a deliberate balance between accessibility for beginners and depth for experts, a tension that has allowed it to dominate the market while leaving competitors scrambling to match its functionality. Understanding its inner workings isn’t just about navigating menus—it’s about grasping the philosophy behind cloud-native operations, where agility and automation are non-negotiable.
The AWS Console’s influence extends beyond technical implementation; it has become a cultural touchstone in the tech industry, setting benchmarks for user experience, security integration, and service integration. Whether you’re a seasoned architect or a newcomer to cloud computing, its impact is undeniable—it’s the bridge between raw computational power and real-world business outcomes.

The Complete Overview of the AWS Console
The AWS Console serves as the primary gateway to Amazon’s sprawling cloud ecosystem, consolidating over 200 services into a single, cohesive interface. At its core, it functions as a command center where users interact with virtual servers, storage systems, databases, and AI tools through a unified dashboard. This consolidation eliminates the need for disparate management tools, reducing operational overhead and accelerating deployment cycles. The console’s design prioritizes modularity, allowing users to focus on specific tasks—such as launching an EC2 instance or configuring a Lambda function—without wading through irrelevant options.What sets the AWS Console apart is its dynamic adaptability. The interface evolves alongside AWS’s service portfolio, introducing new features like the AWS Management Console’s "Quick Start" templates or the enhanced navigation pane that categorizes services by use case (Compute, Storage, Databases, etc.). This structured approach ensures that even as AWS expands, users retain a sense of familiarity, mitigating the learning curve associated with complex cloud environments. The console’s responsiveness—whether accessed via web browser, CLI, or SDKs—further solidifies its role as the linchpin of AWS’s infrastructure-as-code philosophy.
Historical Background and Evolution
The AWS Console’s origins trace back to 2006, when Amazon first unveiled its cloud computing platform as a spin-off of its internal infrastructure tools. Early versions were rudimentary by today’s standards, offering basic controls for S3 storage and EC2 virtual machines. However, the console’s true evolution began in the late 2000s as AWS recognized the need for a more intuitive interface to compete with emerging cloud providers. By 2011, the introduction of the "AWS Management Console" marked a turning point, introducing a unified dashboard that streamlined service access and reduced reliance on command-line interfaces.The console’s trajectory has been marked by iterative improvements driven by user feedback and technological advancements. In 2015, AWS launched the "AWS Personal Health Dashboard," providing real-time insights into service health and maintenance events—a feature that became a standard in cloud monitoring. Subsequent updates, such as the 2018 release of the "AWS Console Mobile Application," extended accessibility to on-the-go professionals. More recently, AWS has integrated machine learning-driven recommendations (e.g., "AWS Personalized Views") and role-based access controls (RBAC) to enhance security and efficiency. Each iteration reflects AWS’s commitment to balancing innovation with backward compatibility, ensuring the console remains both cutting-edge and dependable.
Core Mechanisms: How It Works
Under the hood, the AWS Console operates as a thin client that communicates with AWS’s global infrastructure via secure APIs and SDKs. When a user initiates an action—such as creating a VPC or adjusting IAM policies—the console translates these inputs into RESTful API calls, which are then processed by AWS’s backend systems. This separation of concerns allows the console to remain lightweight while offloading heavy computations to distributed servers. The use of HTTPS ensures encrypted communication, while AWS’s identity and access management (IAM) system authenticates users through temporary security credentials, reducing exposure to hardcoded secrets.Table of Contents
- The Complete Overview of the AWS Console
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can I access the AWS Console without an AWS account?
- Q: Is the AWS Console secure for enterprise use?
- Q: How does the AWS Console handle multi-region deployments?
- Q: Are there alternatives to the AWS Console for managing AWS services?
- Q: How can I customize the AWS Console for my team?
- Q: What happens if AWS experiences an outage affecting the console?
The console’s performance is further optimized through regional endpoints and edge caching. Users interact with the closest available AWS region, minimizing latency, while static assets (like UI components) are cached globally via Amazon CloudFront. Behind the scenes, AWS employs a microservices architecture, where each service (e.g., S3, RDS) maintains its own API and data plane, but the console unifies these under a single pane of glass. This modularity enables AWS to add or modify services without disrupting the entire ecosystem—a critical advantage in the fast-paced cloud market.
Key Benefits and Crucial Impact
The AWS Console’s influence on cloud computing cannot be overstated. It has democratized access to enterprise-grade infrastructure, allowing startups and Fortune 500 companies alike to leverage AWS’s global network without the need for on-premises hardware. By abstracting low-level details, the console lowers the barrier to entry, enabling non-experts to deploy complex architectures with minimal training. This accessibility has fueled AWS’s market dominance, with the console serving as the de facto standard for cloud management interfaces.Beyond its technical merits, the AWS Console has reshaped organizational workflows. Teams now collaborate in real time, sharing permissions and resources through fine-grained IAM policies. Auditing and compliance are simplified via AWS CloudTrail, which logs console activity for governance and security reviews. The console’s integration with third-party tools (e.g., Terraform, Ansible) further extends its utility, embedding AWS into DevOps pipelines and CI/CD workflows.
"The AWS Console isn’t just a tool—it’s the operational backbone of modern cloud-native applications. Its ability to scale from a single developer’s project to a multinational deployment is unparalleled." — AWS Senior Architect, 2023
Major Advantages
- Unified Access: Consolidates 200+ AWS services into a single interface, eliminating the need for multiple dashboards or CLI tools.
- Granular Control: Role-based permissions and resource-level policies ensure least-privilege access, enhancing security without sacrificing flexibility.
- Real-Time Monitoring: Integrated tools like CloudWatch and Trusted Advisor provide actionable insights into performance, costs, and security posture.
- Cross-Service Workflows: Features like AWS Step Functions and EventBridge enable automated, multi-service orchestration directly from the console.
- Global Scalability: Regional endpoints and edge caching ensure low-latency access regardless of user location or AWS region.

Comparative Analysis
While the AWS Console is industry-leading, other cloud providers offer competing interfaces with distinct strengths. Below is a side-by-side comparison of key features:| Feature | AWS Console | Azure Portal | Google Cloud Console |
|---|---|---|---|
| Service Integration | 200+ native services with deep interoperability (e.g., Lambda → S3 triggers). | 100+ services with strong Microsoft ecosystem integration (e.g., Active Directory). | 100+ services with Google Workspace and AI/ML focus (e.g., Vertex AI). |
| Customization | Personalized views, saved filters, and third-party plugin support (via AWS Marketplace). | Custom dashboards and PowerShell integration for enterprise admins. | Modular panels and Jupyter Notebook integration for data scientists. |
| Security Model | IAM with temporary credentials, SCPs, and AWS Organizations for hierarchical policies. | Azure AD integration, conditional access, and Microsoft Defender for Cloud. | Google Cloud IAM with attribute-based access control (ABAC) and BeyondCorp. |
| Learning Curve | Steep for beginners but extensive documentation and training (AWS Skill Builder). | Easier for Windows/Microsoft-centric teams; requires .NET knowledge for advanced use. | Favors developers with Linux/Google Cloud expertise; less intuitive for non-tech users. |
Future Trends and Innovations
The AWS Console is poised to evolve in response to three major trends: AI-driven automation, edge computing, and sustainability. AWS is already embedding generative AI tools (e.g., AWS Bedrock) into the console to assist with infrastructure-as-code generation and troubleshooting. Future iterations may include natural language queries for service configuration, reducing reliance on manual CLI commands. Meanwhile, the console’s support for AWS Local Zones and Outposts will expand, offering seamless management of hybrid and edge deployments—a critical need for industries like manufacturing and healthcare.Sustainability will also play a larger role, with the console incorporating carbon-aware computing features (e.g., workload placement based on renewable energy availability). AWS’s commitment to reducing its carbon footprint by 80% by 2025 will likely translate into new console metrics and optimization recommendations. As quantum computing matures, expect the AWS Console to introduce quantum-specific tools, further cementing its position as the most forward-looking cloud management platform.
Conclusion
The AWS Console is more than a utility—it’s a testament to how thoughtful design and relentless innovation can redefine an entire industry. Its ability to simplify complexity while accommodating scalability has made it indispensable for organizations of all sizes. As cloud computing continues to blur the lines between infrastructure and application development, the console’s role will only grow, serving as the hub where human intent meets machine execution.For businesses, the takeaway is clear: mastering the AWS Console isn’t optional; it’s a strategic imperative. Whether through automation, security hardening, or cost optimization, the console empowers teams to build, deploy, and scale with confidence. In an era where digital transformation hinges on cloud agility, the AWS Console remains the most reliable compass for navigating the future of computing.
Comprehensive FAQs
Q: Can I access the AWS Console without an AWS account?
A: No. The AWS Console requires a valid AWS account, which can be created for free (with limited services) or upgraded to a paid plan for full access. Account creation involves verifying identity via email, phone, or government-issued ID, depending on the region.
Q: Is the AWS Console secure for enterprise use?
A: Yes. AWS employs industry-standard encryption (TLS 1.2+) for data in transit and at rest, alongside IAM for granular permissions. Enterprises can further enhance security with AWS Organizations, AWS Config for compliance monitoring, and AWS GuardDuty for threat detection.
Q: How does the AWS Console handle multi-region deployments?
A: The console supports multi-region operations through AWS Global Accelerator and Route 53 for DNS management. Users can deploy resources in multiple regions simultaneously and monitor them via CloudWatch’s global metrics. However, cross-region data replication (e.g., for databases) requires additional services like AWS DMS.
Q: Are there alternatives to the AWS Console for managing AWS services?
A: Yes. AWS offers the AWS CLI for scripted automation, AWS SDKs for custom applications, and third-party tools like Terraform or Pulumi for infrastructure-as-code. Some users also rely on AWS CloudShell, a browser-based terminal, for lightweight management tasks.
Q: How can I customize the AWS Console for my team?
A: Customization options include:
- Creating personalized views to prioritize frequently used services.
- Using AWS SSO for centralized identity management.
- Integrating third-party plugins via AWS Marketplace.
- Configuring default regions and resource tags for consistency.
Q: What happens if AWS experiences an outage affecting the console?
A: AWS has a multi-layered redundancy strategy to minimize console outages. If the web interface becomes unavailable, users can fall back to the AWS CLI, SDKs, or direct API calls. AWS also provides a Service Health Dashboard to track incidents in real time.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Gouv.